LLM & GenAI Security
Protect Enterprises from misuse and exfiltration of Data through LLMs with Policy Based Access Control
Secure Policy-Driven AI Data Access
Protect sensitive data and enforce compliance with PlainID’s Policy-Based Access Control (PBAC). Whether through AI agents (NHIs) or GenAI-driven insights, access must be tied to the user’s identity, ensuring permissions align with roles and policies. With real-time authorization, PlainID safeguards proprietary data across Retrieval-Augmented Generation (RAG) and Large Language Models (LLMs), maintaining Zero Trust and regulatory compliance.
Control AI-Generated Responses and AI Agents to Prevent Data Leaks and Ensure Compliance
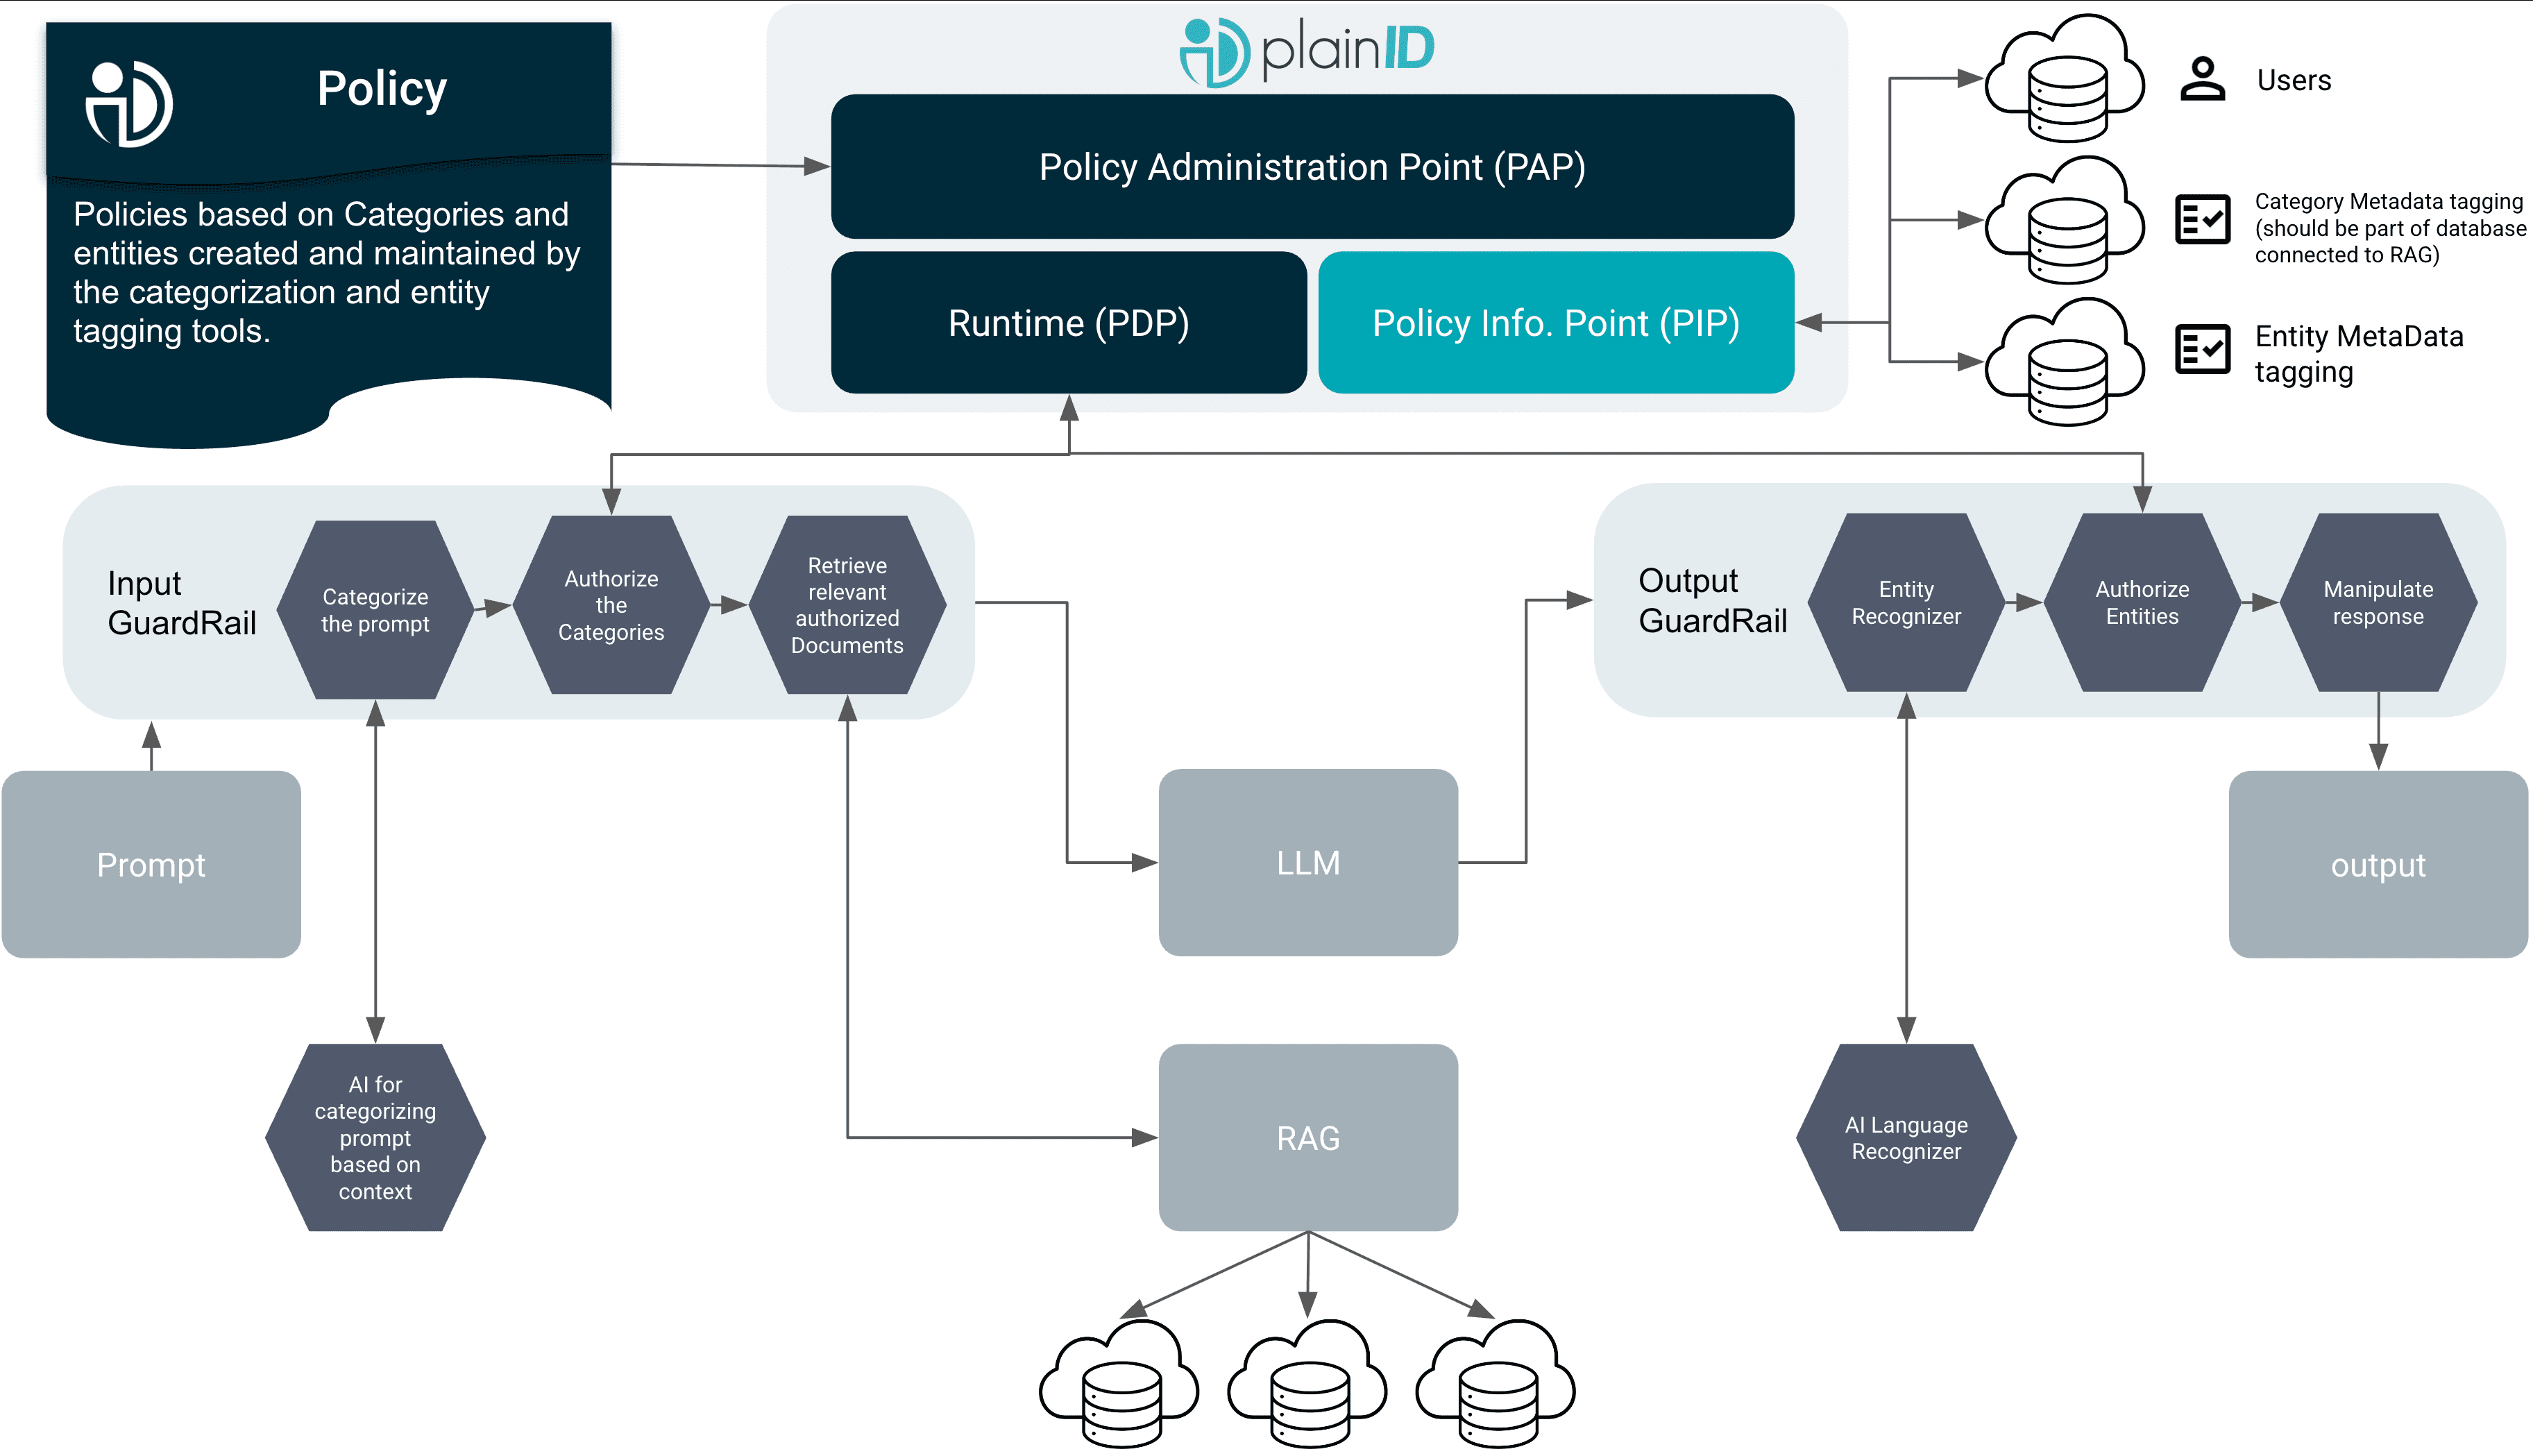
Secure AI Query Input
Enforce query authorization to ensure users can only ask questions within their authorized scope. Prevent unauthorized attempts to extract sensitive or restricted information.
Control Data Retrieval
Apply policy-based controls to restrict which data and documents AI can retrieve to generate insights from Retrieval-Augmented Generation (RAG) systems.
LLM Response Filtering and Masking
Enforce authorization at the response layer, ensuring that even after data is retrieved, AI-generated outputs are controlled to prevent expose of sensitve data.
Download the Whitepaper
Learn about Enhancing Data Security with Dynamic Authorization.
Loading form…
Related Resources


Explore the Platform
One Platform to Provide you Visibility, Central Policy Management, and Dynamic Authorization.