PlainID vs. Palo Alto's Idira for Agentic AI Authorization
Idira governs who has access. PlainID controls what AI agents can do with it.
What will you do when:
- Your AI agent has scoped privileges
- but retrieves 10x more data than the task requires
- Access was provisioned correctly
- but no one enforced what it did at runtime
- You know which agents exist
- but you cannot explain every action they took and why it was allowed
Idira was built for privilege management while PlainID was built for runtime authorization.
Idira discovers identities, scopes privileges, and governs the access lifecycle. That is important work. But it is not the same as runtime authorization.
Privilege management determines what an identity is allowed to access before a session begins. Runtime authorization determines whether a specific action is permitted at the exact moment it is attempted — with live context, applied to every step of an agent's workflow.
When an AI agent is mid-task, Idira has already done its job. PlainID is the layer that governs what the agent can access, do and expose.

Authorization as the Control Plane
With PlainID every action every identity takes, human, machine, or AI agent, is evaluated against policy at the moment of execution. Not at provisioning. At the moment of access.

Full AI Flow Coverage
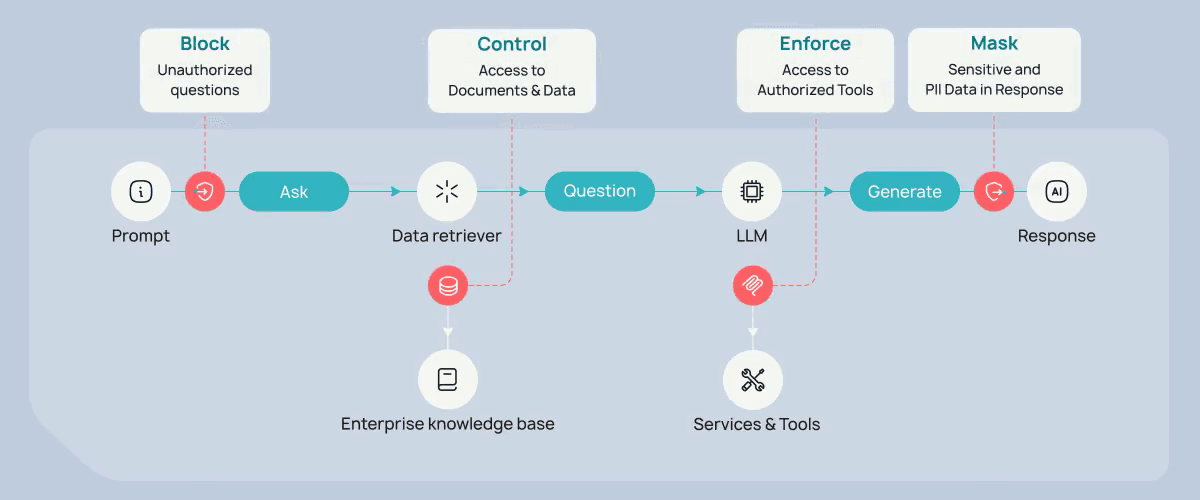
PlainID enforces authorization across the complete agentic workflow: user intent and prompt, data retrieval, tool and MCP access, and output before delivery. Idira governs access to the flow. PlainID governs the flow itself.
Continuous Zero Standing Privileges
With PlainID access is granted just-in-time, scoped to the specific action, and revoked immediately after. No long-lived privileges. No assumption that what was provisioned at the start remains safe at every step.
Native Enforcement - Not an Integration
Idira's agentic controls are dependent on Prisma AIRS integration. PlainID's enforcement is native: same policy engine, same Authorizer suite, same audit trail, across APIs, data platforms, and AI agent frameworks, out of the box.
How PlainID Is Different From Idira for Agentic AI
Discover why Fortune 500 enterprises trust PlainID to securely scale agentic AI systems:
Full coverage: Every step of the agent workflow
Enforces authorization across every step of the agent workflow: input, data retrieval, tools/MCP, output
Gap / limitation: Access at provisioning
Governs access to the agentic environment at provisioning
Full coverage: Runtime, per action
Runtime authorization: every action evaluated at the moment it is attempted, with live context
Gap / limitation: Dynamic privilege management
Dynamic privilege management: grant, scope, revoke
Full coverage: Native Authorizer suite
Native Authorizer suite covering APIs, data platforms, microservices, and AI agent frameworks — no integration burden
Gap / limitation: Via Prisma AIRS, a separate product
Enforcement through Prisma AIRS integration (separate product)
Full coverage: Human and agent bound together
Binding of human and agent identities in every policy decision — neither exceeds the other's real-time entitlements
Gap / limitation: Discovery and governance
Discovery and governance of human, machine, and agent identities
Full coverage: Zero Standing Privileges at runtime
Zero Standing Privileges enforced at runtime — access evaluated per action, not assumed from provisioning
Gap / limitation: Scoped privileges limit blast radius
Scoped privileges reduce the blast radius of a compromised identity
Full coverage: Explainable, per decision
Full explainability for every authorization decision: policy evaluated, context applied, action allowed or denied, at agent speed, at enterprise scale
Gap / limitation: Grants and lifecycle events
Audit trail for access grants and lifecycle events
- Full coverage
- Partial coverage
- Gap / limitation
Idira grants access. PlainID controls what agents do with it.
Idira can tell you that an AI agent has been granted access to a data source. That is necessary. It is not sufficient.
At the moment the agent acts, retrieving a record, calling a tool, generating a response, the question is not what it was provisioned to access. The question is whether this specific action, in this specific context, against this specific resource, is authorized right now.
That decision must happen in milliseconds. It must account for the identity of the user behind the agent, the agent's current task scope, the sensitivity of the data involved, and the risk level at this moment. Idira does not make that decision. PlainID does.
Authorization must be evaluated every time an action is attempted. Privilege grants are the starting point. Runtime enforcement is the security control.
Data is your most precious asset, but privilege management does not reach the data layer.
Built for Agentic Reality
PlainID's Runtime Authorization Platform is designed for how AI systems actually operate by accessing data, invoking tools, and making decisions across systems in real time.
- Runtime decisioning in place of one-time checks
- Intent-based enforcement tied to every action
- Context-aware policies across APIs, data, and AI
Binding Human and Non-Human Identities
This is the critical control layer missing from traditional IAM. Every decision evaluates:
- The human user
- The AI agent
- The intent of the action
Zero Standing Privileges
Access exists only when it’s needed, and only for the exact purpose it’s required. It’s later revoked immediately after use.
Your AI agents are acting. Are you authorizing every action?
- Trusted by Fortune 500 enterprises to secure millions of identities
- Millions of authorization decisions processed daily
- Built for high-scale, real-time enforcement across complex environments
- Recognized by Gartner and KuppingerCole in authorization and security platforms
GARTNER is a registered trade mark and service mark of Gartner, Inc. and/ or its affiliates in the U.S. and internationally and is used herein with permission. All rights reserved.
Through 2029, over 50% of successful cybersecurity attacks against AI agents will exploit access control issues.
Gartner, How to Secure Custom-Built AI Agents, Dionisio Zumerle, Jeremy D’Hoinne, 11 June 2025
Get control over your AI agents without replacing your IAM
Privilege management determines who can access your environment. Runtime authorization governs what happens inside it, at agent speed, at enterprise scale, at the moment of every action.
See how it works in your environment.
Loading form…
Your AI agents are acting. Are you authorizing every action?
Privilege management determines who can access your environment. Runtime authorization governs what happens inside it, at agent speed, at enterprise scale, at the moment of every action.