ZScaler ZPA
Discover private application access and manage contextual controls through Zscaler ZPA.
About PlainID + ZScaler ZPA
Zscaler Private Access (ZPA) is a cloud-based zero trust network access (ZTNA) solution designed to provide secure remote access to internal applications without exposing them to the internet. It uses identity and context-based access policies to connect users directly to applications over an encrypted connection. This approach helps prevent lateral movement by attackers within the network, reduces the attack surface, and enhances the overall security posture of an organization.
The PlainID Platform supports policy orchestration for Zscaler by allowing PlainID administrators to discover native Zscaler access control policies and enabling visibility, manageability and editability of the Zscaler policies. This integration with Zscaler significantly enhances security by allowing the alignment of network access with application access. With PlainID's policy-based access management, administrators can create fine-tuned access rules that dictate who can access specific applications and under what conditions. When combined with Zscaler's zero trust network access (ZTNA) capabilities, this ensures that only authorized users can connect to the network and access critical applications. The seamless alignment of network and application access policies reduces the risk of unauthorized access, enhances compliance with regulatory requirements, and provides a more secure and efficient way to manage user access in a hybrid or cloud environment. This comprehensive approach to access management helps protect sensitive data and systems from potential breaches while improving user experience through streamlined, context-aware access controls
Technical Information
PlainID Authorizer for ZScaler ZPA is a fully cloud-based solution that does not require organizations to install any type of software, run any services, or create any code. Organizations are a few simple clicks away from getting value out of the PlainID platform. Simple allow PlainID to pull in all existing authorization policies in ZScaler then begin using PlainID to gain full visibility of how your organization works today. After that create new policies using PlainIDs easy to use plain language policy creation tool and let the platform translate these and push them into ZScaler. From then on there will be no guesswork in who can access what endpoints.
Architectures
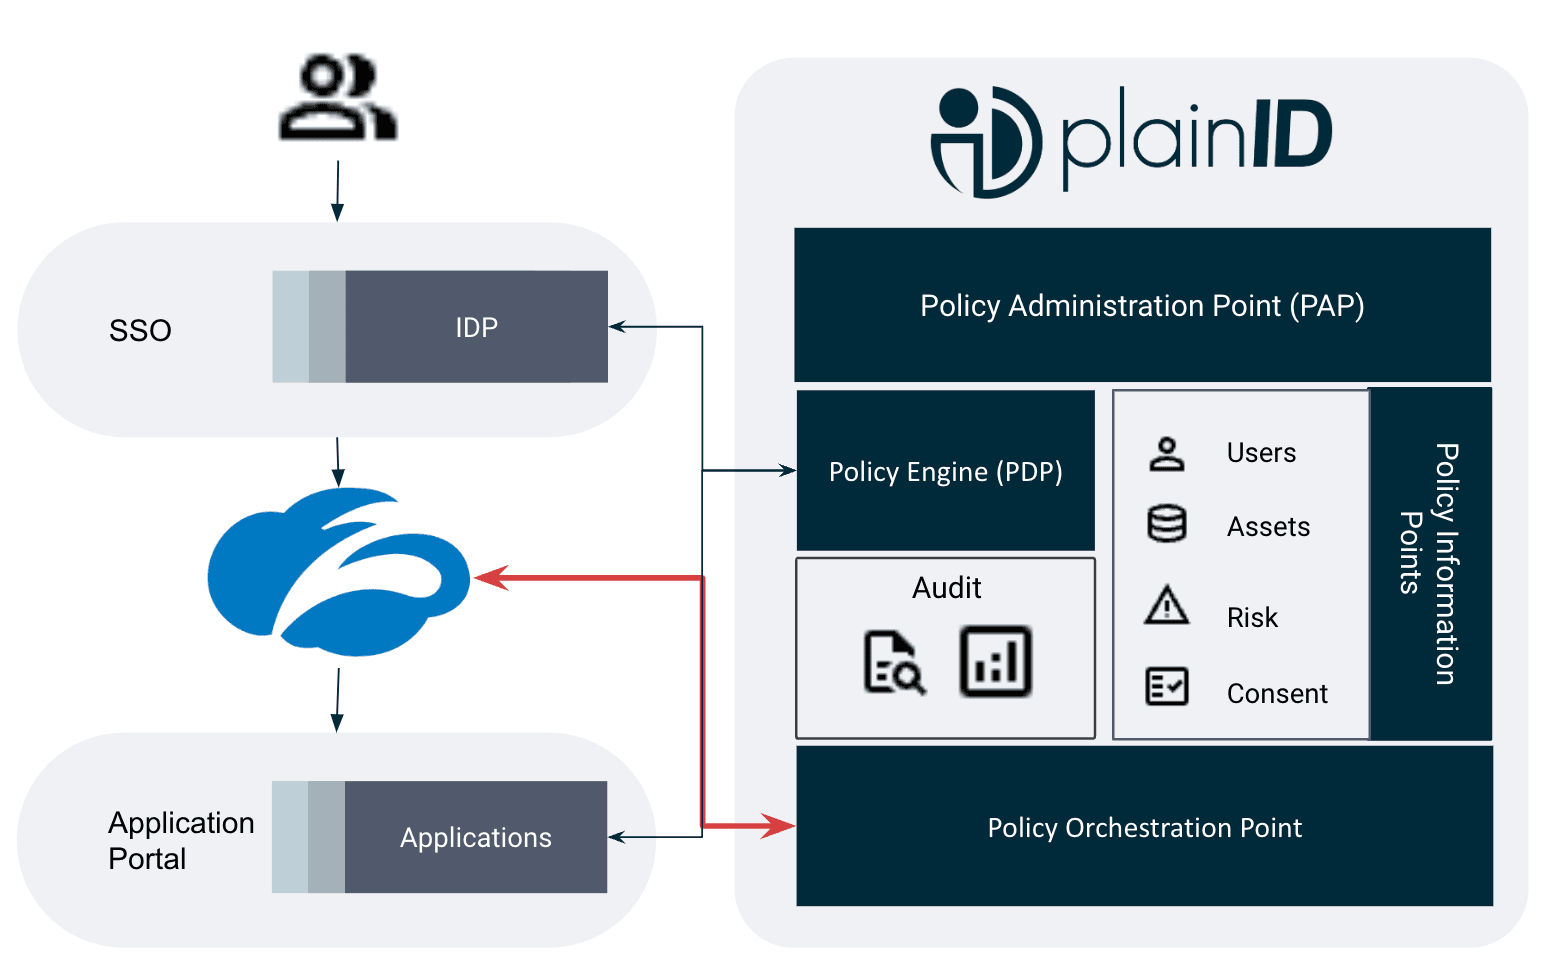
- PlainID connects to Zscaler and learns all current policies for management.
- User request to access critical app is directed to the IDP.
- IDP sends an Authorization request to PlainID to determine user level of access.
- PlainID verify the user has approval, and the list of fine-grained entitlements he is authorized to base on the policies.
- IDP receives the response from PlainID and accordingly enrich the access token.
- The token, enriched with fine-grained entitlements, is passed to the Zscaler.
- ZScaler connects the user to the critical app with read-only access rights
- Optional: Applications receives dynamic fine grained access control decisions from PlainID
Technology
- Other Platforms
Capabilities
- Discover
- Manage
- Enforce
Auth Patterns
- Application Authorization
- Policy Orchestration
Need help integrating?
Our experts can help you architect the perfect authorization strategy for your stack.
Better Together
Connect Context. Centralize Policy. Enforce Everywhere.