Snowflake
Discover Snowflake access and manage fine-grained filtering and masking policies.
About PlainID + Snowflake
Enterprises increasingly rely on Snowflake as a strategic platform for storing, processing, and analyzing vast amounts of data. As data volumes grow and the need for granular access controls increases, ensuring only authorized users can access sensitive information becomes critical.
While Snowflake offers native access control features, aligning these controls across large enterprise environments is complex and error-prone. The challenge many organizations face is that data access policies are often managed in silos. These silos lead to inconsistencies and potential security vulnerabilities, making it difficult for security teams to maintain oversight and ensure sensitive data isn’t inadvertently exposed.
PlainID addresses this gap by centralizing Snowflake’s access controls through a unified Policy-Based Access Control (PBAC) framework. Through Policy Orchestration, the PlainID Platform empowers enterprises to centrally create and manage policies, which are then enforced by Snowflake at the point of data access.
Technical Information
PlainID Authorizer for Snowflake is a fully cloud-based solution that does not require organizations to install any type of software, run any services, or create any code. Organizations are a few simple clicks away from getting value out of the PlainID platform. Simple allow PlainID to pull in all existing authorization policies in Snowflake then begin using PlainID to gain full visibility of how your organization works today. After that create new policies using PlainIDs easy to use plain language policy creation tool and let the platform translate these into Snowflake SQL policies and push them into Snowflake. From then on there will be no guesswork in who can access what data.
Architectures
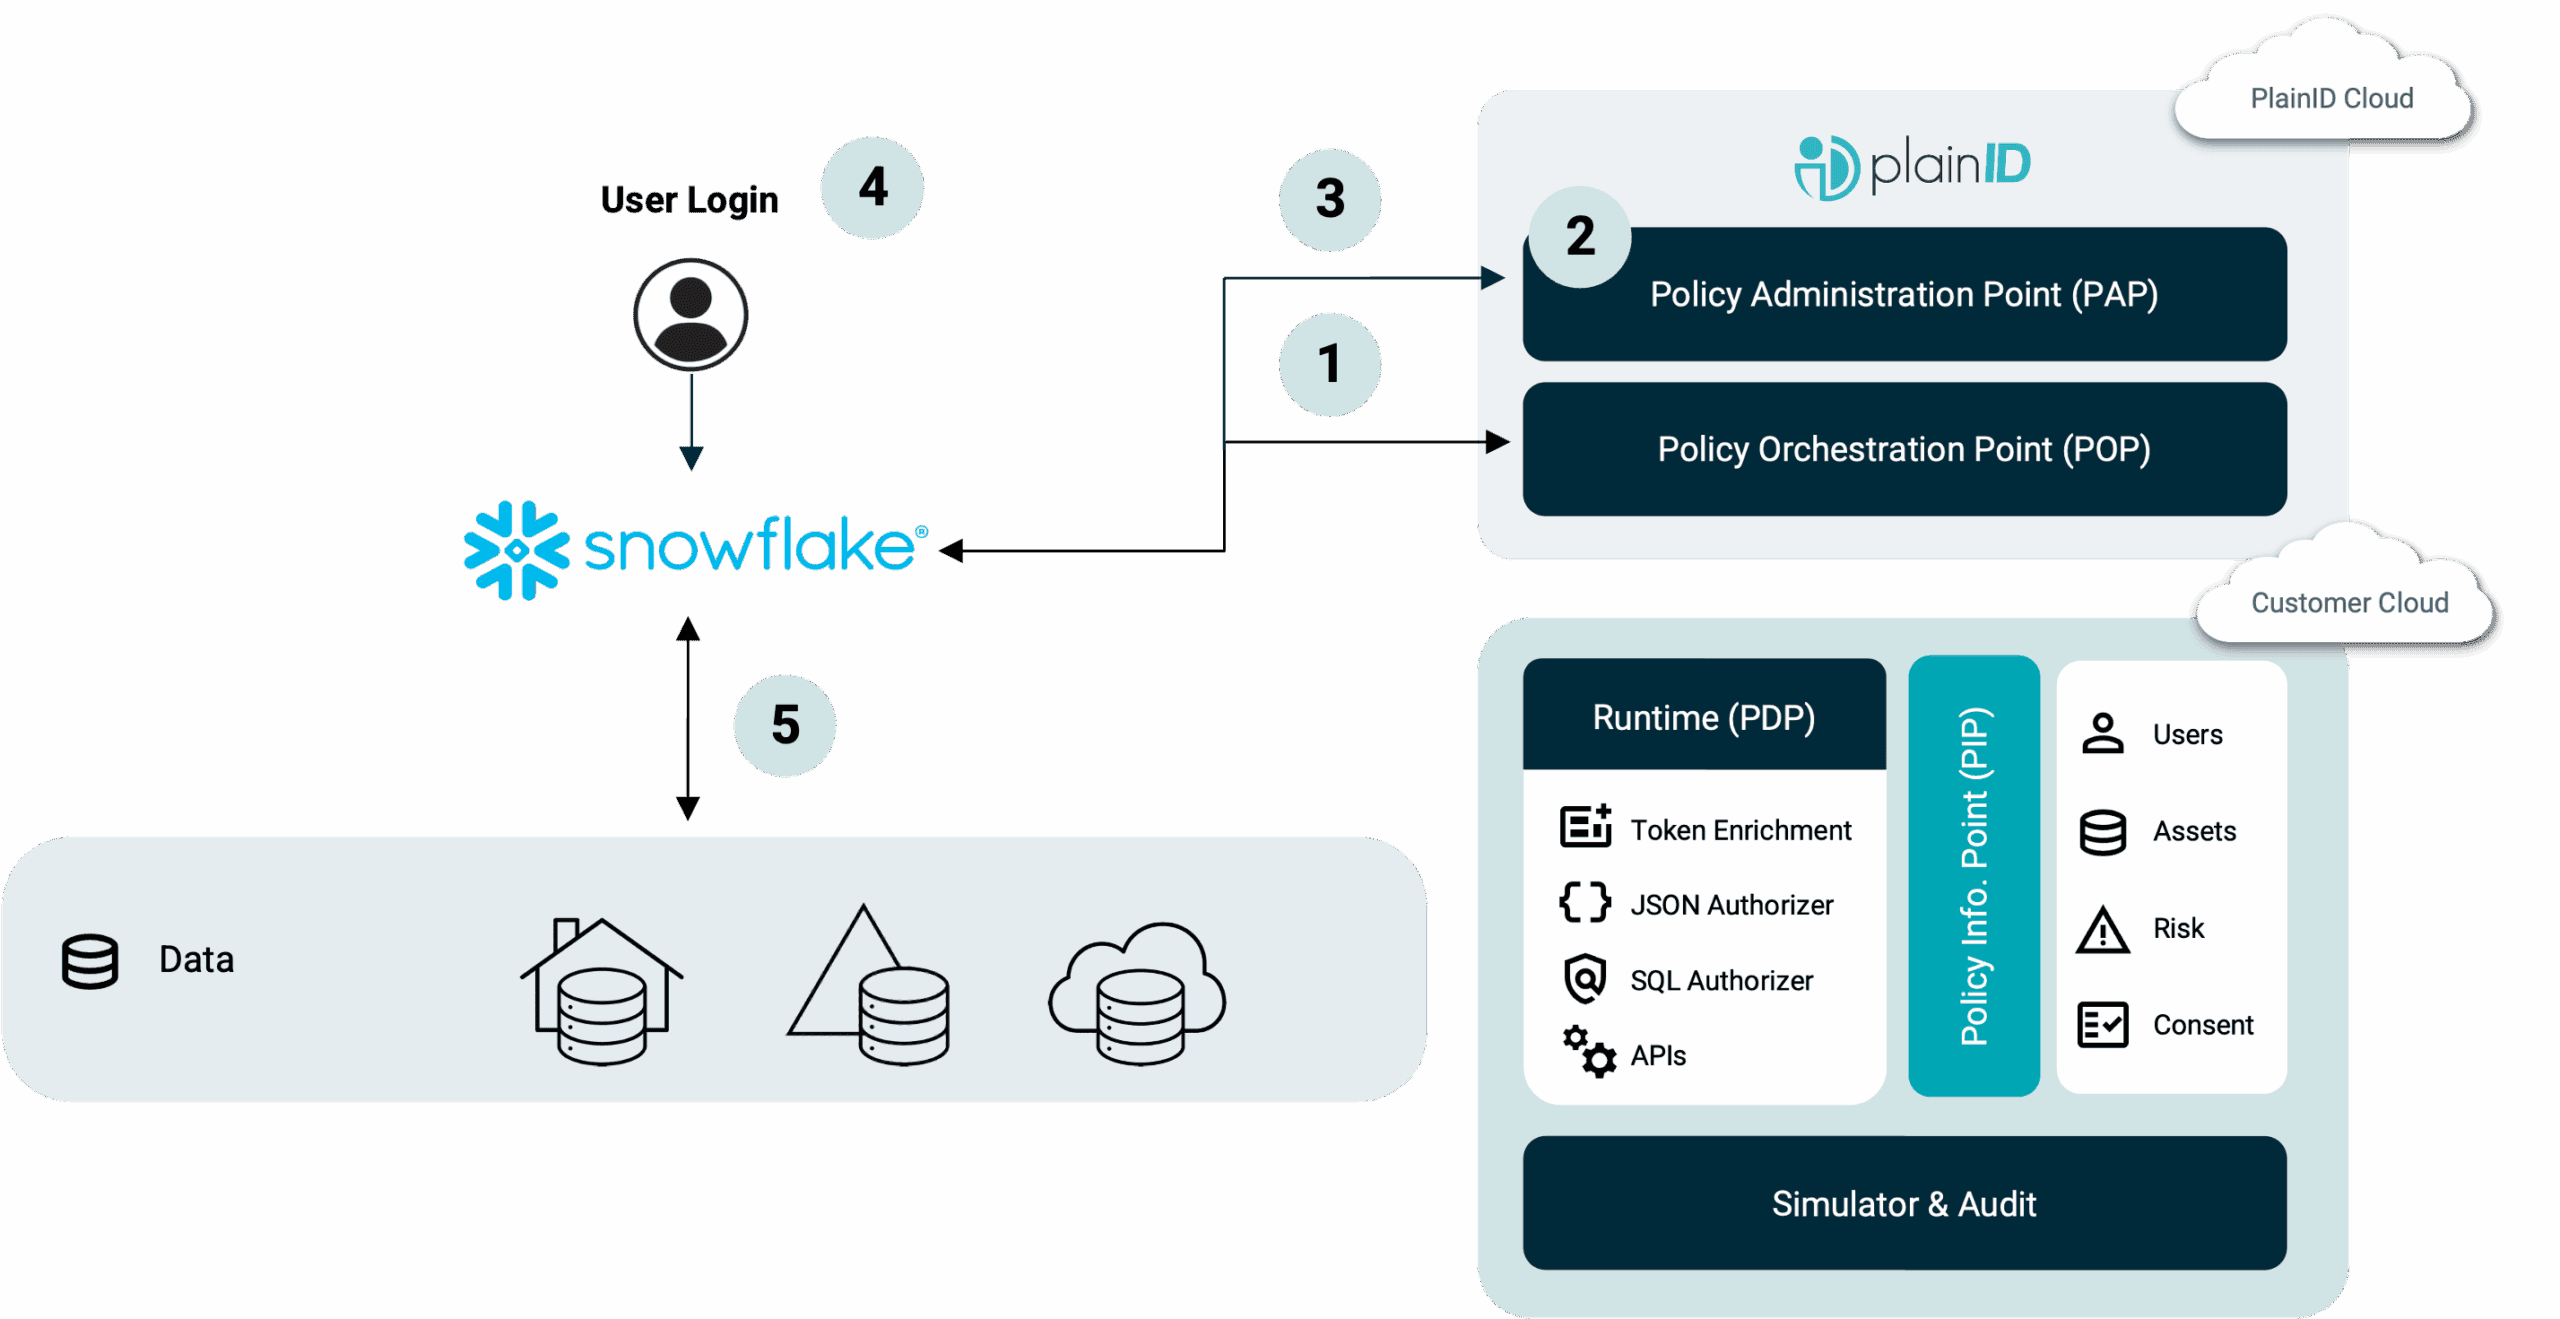
- The PlainID Policy Orchestration Point connects to Snowflake to discover existing policies (row-level access and column masking) and imports them into PlainID.
- Access policies are managed and created centrally in the Policy Administration Point for consistent control across all SaaS vendors.
- Policies are then deployed to the Snowflake platform.
- Users authenticate to Snowflake and request access to tables or data.
- Snowflake enforces access based on PlainID-managed policies, ensuring users see only authorized data.
Technology
- Data platforms
Capabilities
- Discover
- Manage
- Enforce
Auth Patterns
- Data Authorization - Filtering
- Data Authorization - Masking
- Policy Orchestration
- Policy information point (PIP)
Need help integrating?
Our experts can help you architect the perfect authorization strategy for your stack.
Better Together
Connect Context. Centralize Policy. Enforce Everywhere.