OpenClaw
Control OpenClaw agent access to tools, MCP resources, and retrieved content.
About PlainID + OpenClaw
The PlainID OpenClaw Authorizer brings centralized, policy-based authorization to OpenClaw agent workflows through a lightweight native plugin.
Designed for plugin-only deployments, the authorizer allows OpenClaw environments to make real-time PlainID authorization decisions before agents access tools or resolve models. In this mode, the OpenClaw agent itself is evaluated as the primary identity in PlainID, enabling organizations to govern which agents are allowed to perform specific actions across tools, models, and runtime contexts.
This integration is ideal for community, marketplace, and self-managed OpenClaw deployments that need policy-based control without additional sidecar infrastructure. It provides a simple way to extend PlainID authorization into agentic AI workflows while keeping deployment lightweight and operationally straightforward.
Technical Information
The PlainID OpenClaw Authorizer is delivered as a native OpenClaw plugin package and is tested against OpenClaw 2026.3.28. It is designed to be installed directly into an OpenClaw runtime and connected to a PlainID Policy Decision Point for real-time authorization decisions.
The plugin enforces PlainID authorization during key OpenClaw runtime events, including tool invocation and model resolution. This allows organizations to control agent behavior at critical decision points, such as whether an agent can invoke a specific tool or access a specific model.
Recommended Use Cases
The PlainID OpenClaw Authorizer is recommended for organizations that want to:
- Apply centralized authorization policies to OpenClaw agents.
- Control which agents can access specific tools.
- Govern model access based on agent identity.
- Add policy-based guardrails to agentic AI workflows.
- Deploy authorization without operating sidecar infrastructure.
- Support marketplace or community OpenClaw installations with minimal operational complexity.
Architectures
Usage Example
An organization uses OpenClaw to run multiple AI agents, each responsible for a different business function.
The PlainID OpenClaw Authorizer is installed as a native OpenClaw plugin.
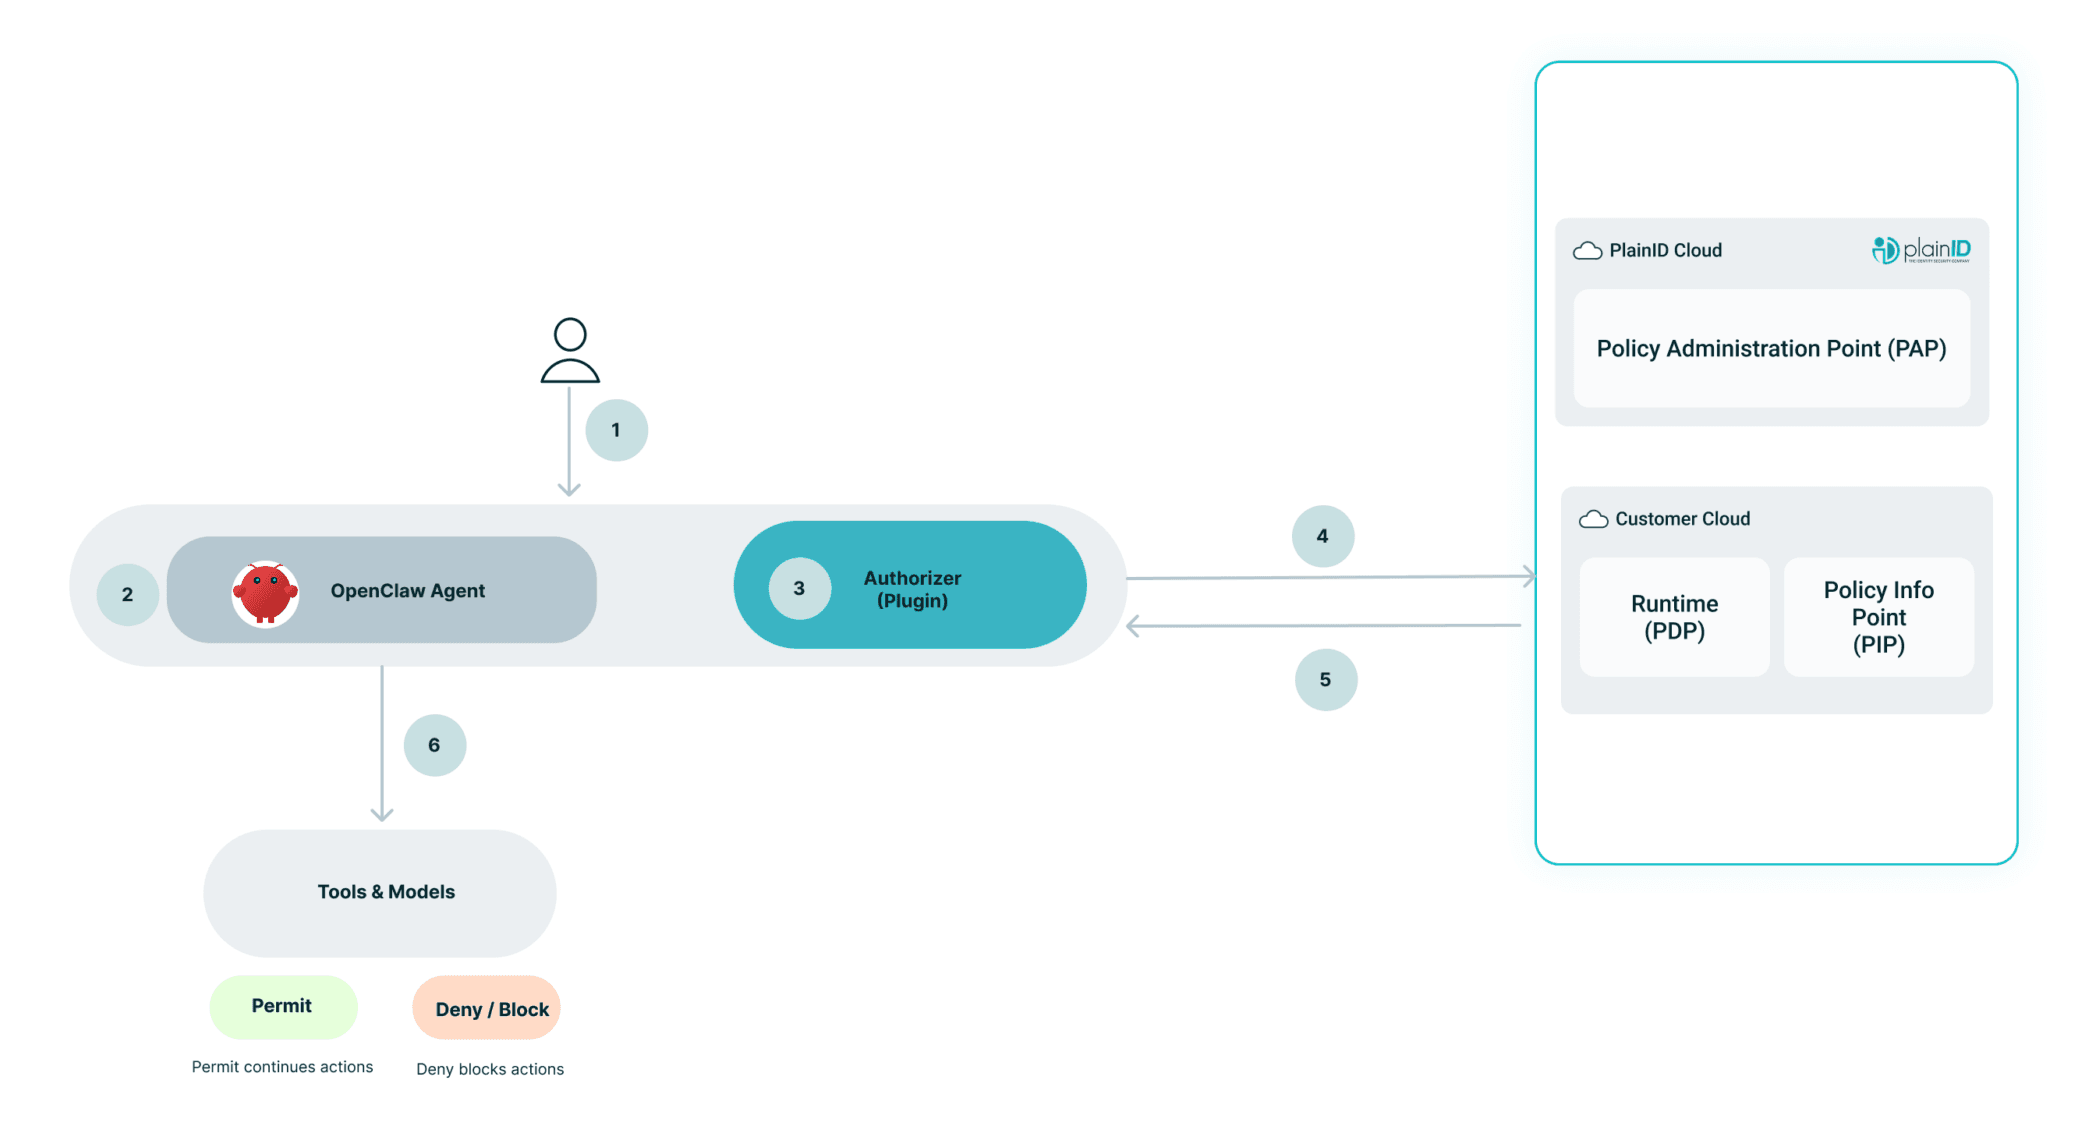
- A user submits a request to an OpenClaw agent.
- OpenClaw starts processing the request and prepares to use a model or invoke a tool.
- Before the model is resolved or the tool is called, the PlainID OpenClaw Authorizer plugin
intercepts the runtime event. The plugin identifies the OpenClaw agent involved in the action,
such as finance-assistant. - The plugin sends the agent identity and requested action context to PlainID for authorization.
PlainID evaluates the request against configured policies. - The access decision is returned to the plugin.
- If the policy permits the action, OpenClaw continues and the agent can use the requested model
or tool. If the policy denies the action, the plugin blocks the operation before the model is
resolved or the tool is invoked.
Technology
- Agentic Platforms
Capabilities
- Manage
- Enforce
Auth Patterns
- MCP Authorizations
- Agentic Authorizations (Guardrails)
- RAG Authorizations
Need help integrating?
Our experts can help you architect the perfect authorization strategy for your stack.
Better Together
Connect Context. Centralize Policy. Enforce Everywhere.