ForgeRock
Use ForgeRock identity context and enrich its tokens to drive fine-grained access decisions.
About PlainID + ForgeRock
The integration between PlainID and ForgeRock enables organizations to apply a continuous Authentication-Authorization process. The PlainID ForgeRock Authorizer will continue the Authentication process carried out by ForgeRock, to provide the full adaptive access the user is entitled for.
The main objective of ForgeRock, as an IdP (Identity provider), is to handle the authentication process, this is mostly done based on well-defined protocols such as OIDC and SAML. The outcome of the process is an authentication token. During the Authentication process, the PlainID ForgeRock Authorizer dynamically calculates and provides a list of claims and groups based on the policies defined within PlainID. These claims and groups will be used to enrich the token-minted ForgeRock. The objective of the token enrichment flow is to dynamically and contextually calculate and provide the list of claims (Authorizations) to ForgeRock, as part of the login process.
Technical Information
The PlainID ForgeRock Authorizer allows PlainID to enrich ForgeRock's JWT as part of the login process. This is done by utilizing ForgeRock’s Custom Claims Groovy Script to obtain the relevant claims for the authenticating user from PlainID’s PDP. The Token Enrichment functionality is supported both by the PlainID Cloud-Based PDP, and the Hybrid, customer-hosted PlainID Policy Authorization Agent.
Architectures
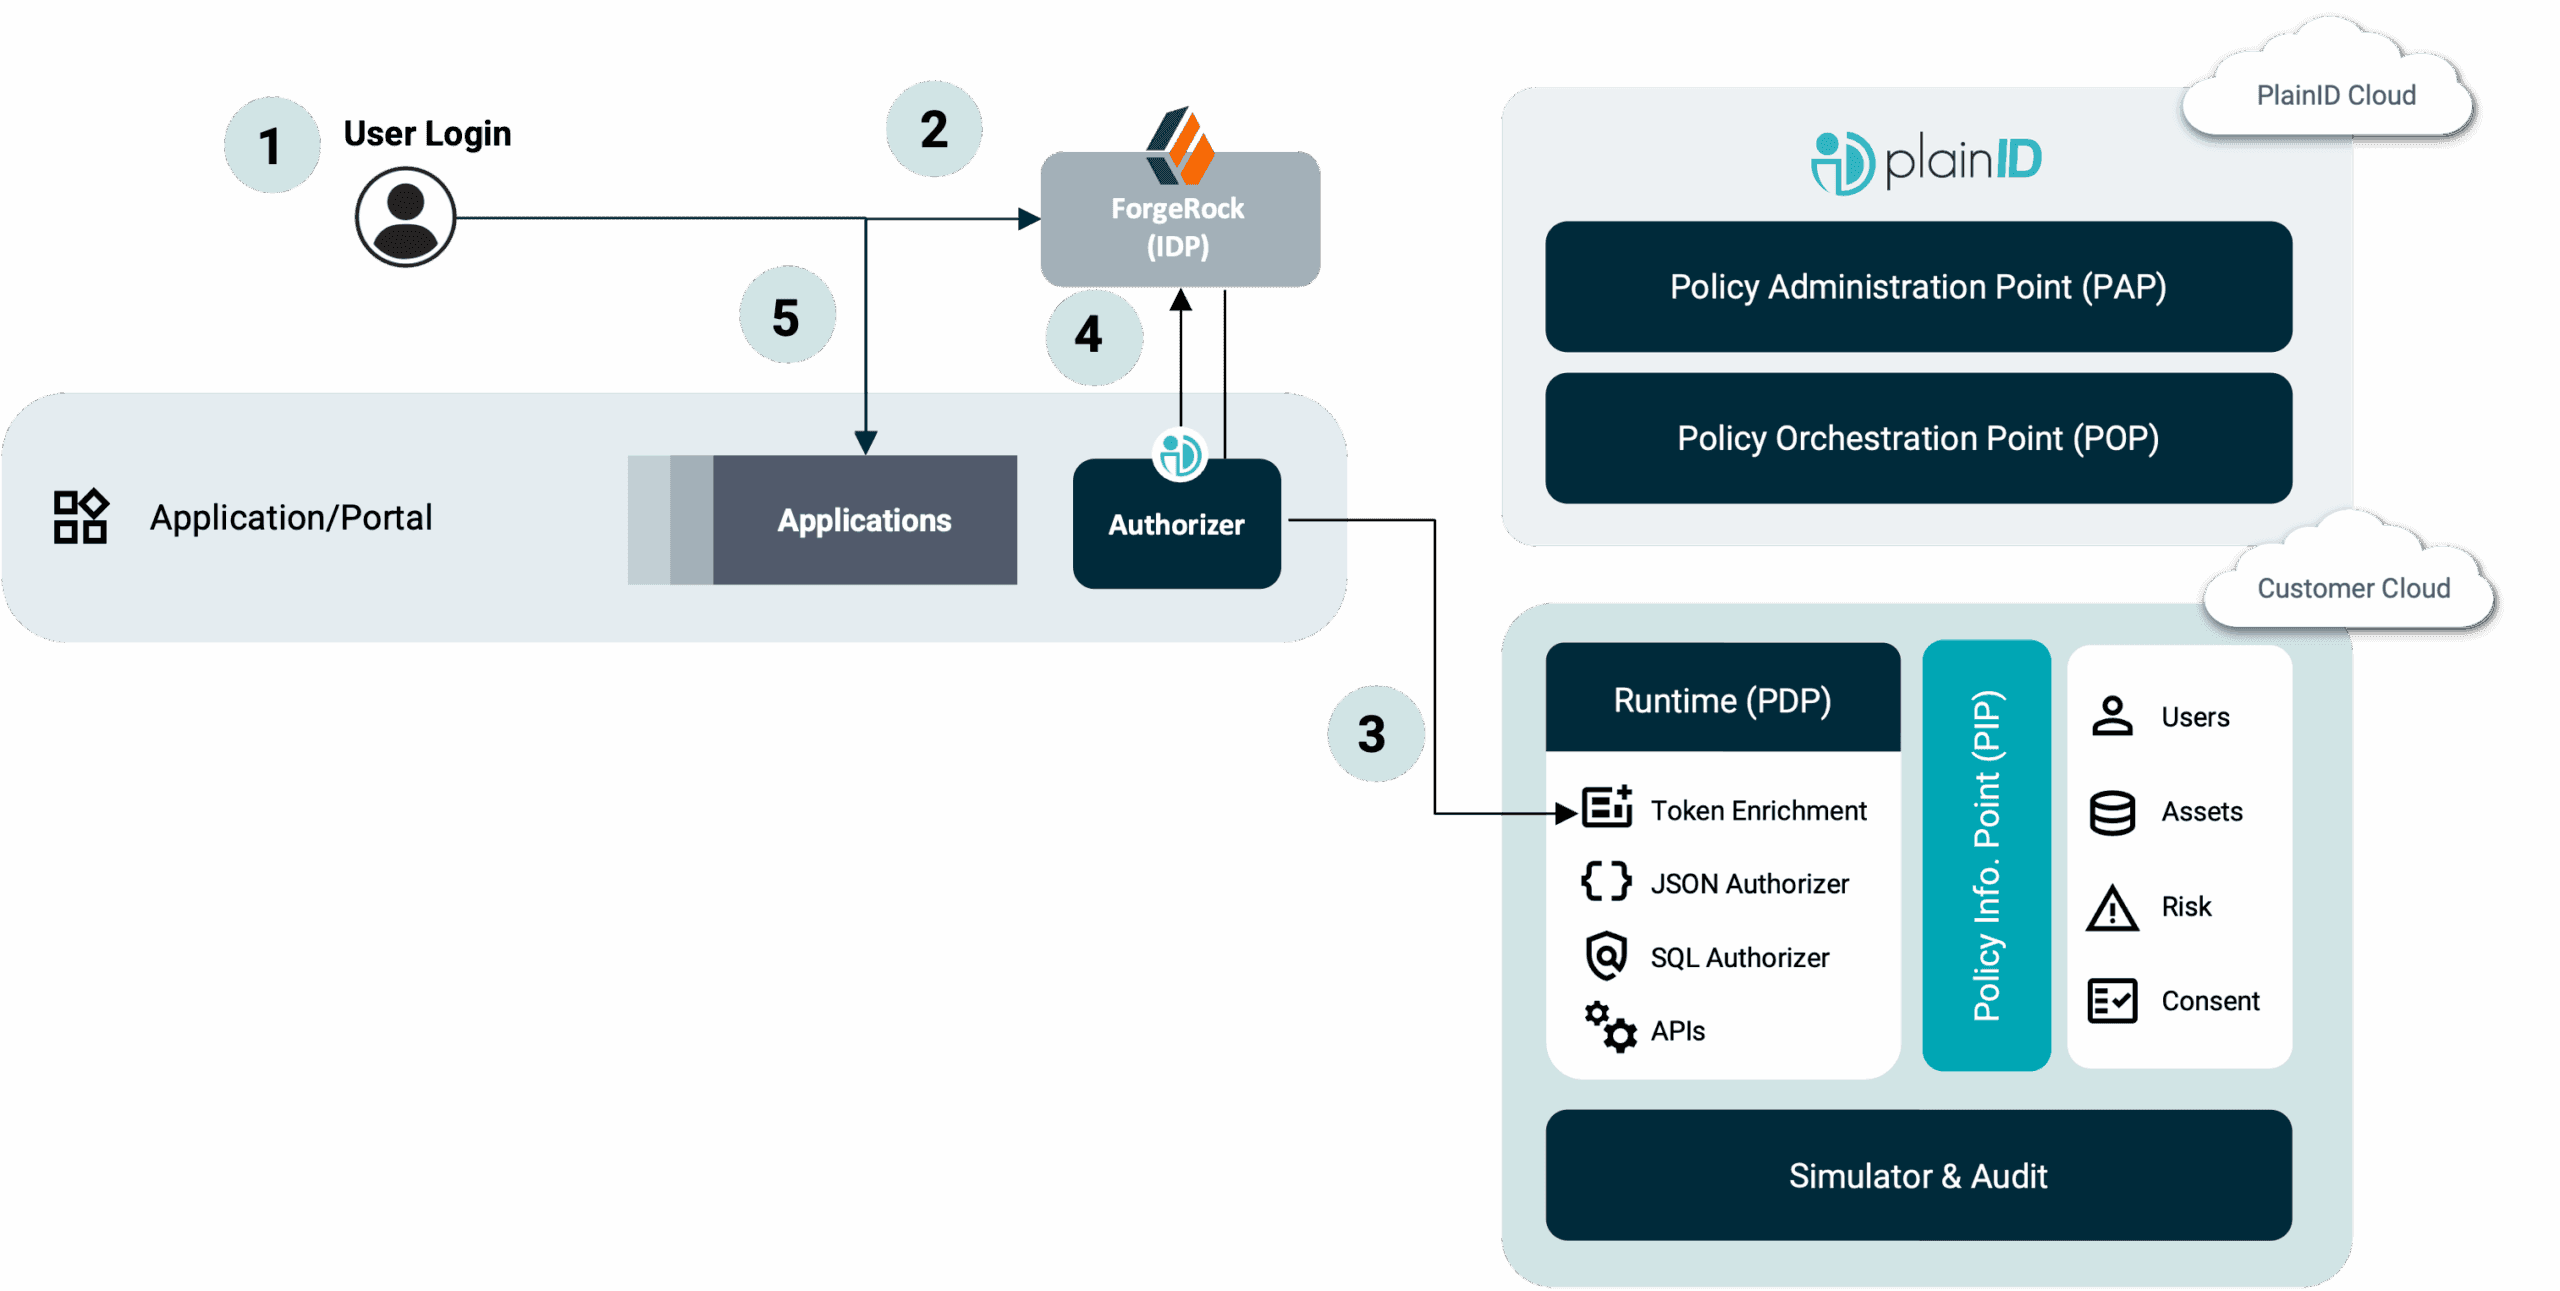
- User attempts to access the application and is redirected to ForgeRock (IdP)
- ForgeRock Authenticates the user and reaches out to PlainID Authorizer to determine which Claims should be embedded in the token.
- The PDP dynamically calculates the access decision, utilizing the Policy Information Point (PIP) to retrieve additional user or asset attributes from various data sources if required. The PlainID Authorizer then returns access decisions along with claims that enrich the access token minted by ForgeRock.
- ForgeRock sends the user with the new JWT token to the application and the application consumes the token
Technology
- Identity Providers
Capabilities
- Manage
- Enforce
Auth Patterns
- Token Enrichment
- Policy information point (PIP)
Need help integrating?
Our experts can help you architect the perfect authorization strategy for your stack.
Better Together
Connect Context. Centralize Policy. Enforce Everywhere.