Amazon API Gateway
Discover API and agent activity and enforce contextual access through Amazon API Gateway.
About PlainID + Amazon API Gateway
API access control is a crucial aspect of ensuring the overall security of your APIs including the data and functionality they provide. Central to this is the need to be aware of the business context of the API usage, which includes the end-user on behalf of the request is made, and what function and data it is asked to provide.
For example, in a commercial banking application, this will mean making a decision based on the bank teller who's trying to access the bank account, which branch he is part of, what is his title, etc. And the actual bank account he is asking to access, the type or status of the account, and more.
The decision can’t be based just on the service account that is using that specific API. Though API Gateways do have access control capabilities, usually they are unaware of the context (i.e. will make a decision to determine if a call for a service can be made, and not based on the specific context of the call), and whatever identity-awareness they might have is limited and hard to manage.
Without contextual and identity-aware measures in place, there are significant risks associated with unauthorized access to the data through APIs.
PlainID Authorizer for AWS API gateways provides the API gateway with context awareness, of the identity and the assets the identity is trying to access.
Technical Information
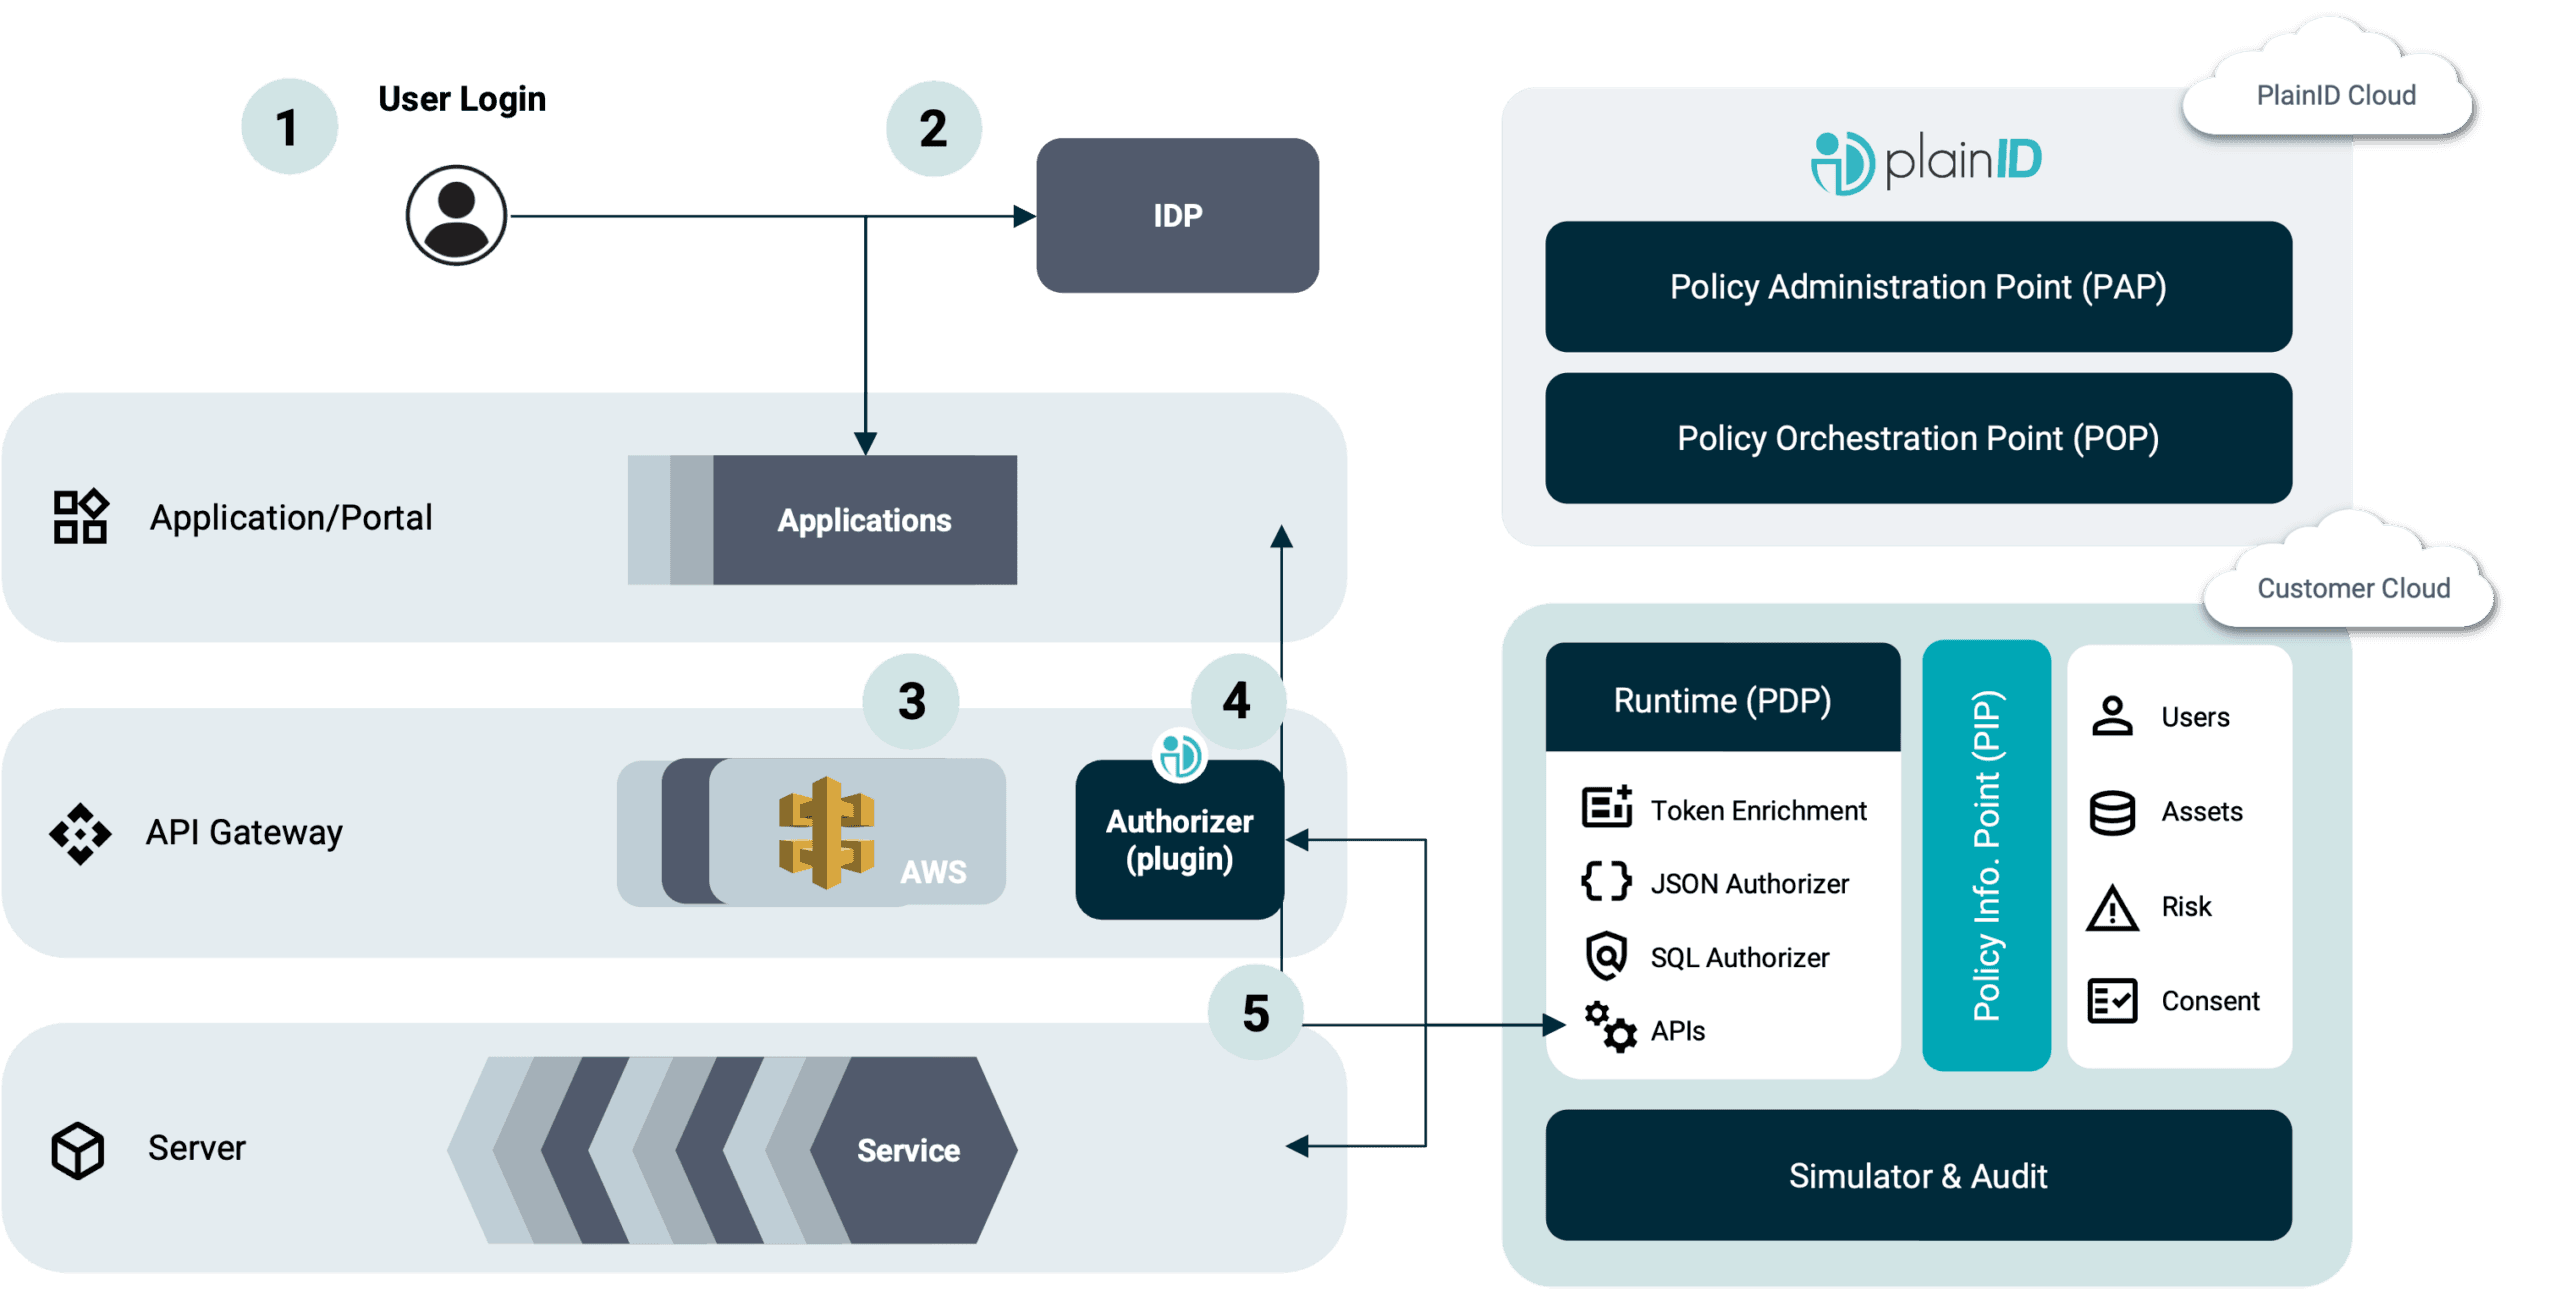
The PlainID AWS API Gateway Authorizer is utilizing an AWS Authorization Lambda. It serves as a middleware that sends Policy Decision Requests to the Policy Decision Point (PDP) when resource access is being attempted by an application, user, or service via the API gateway. The Authorizer then returns the decision made by the PDP to the API Gateway - to either permit or deny access to the resource.
Architectures
- The end user accesses the app.
- The user is redirected to complete the authentication process on the Identity Provider (IdP).
- The application accesses services/APIs in AWS. The API call is intercepted by the AWS API GW.
- The PlainID Authorizer plugin in the API Gateway receives requests, queries the PlainID PDP for access decisions based on configured policies, and enforces them by permitting or denying the requests.
- The API call is passed on to the service layer
Technology
- API Gateways
- MCP/AI Gateways
Capabilities
- Discover
- Manage
- Enforce
Auth Patterns
- MCP Authorizations
- Agentic Authorizations (Guardrails)
- API Authorization
Need help integrating?
Our experts can help you architect the perfect authorization strategy for your stack.
Better Together
Connect Context. Centralize Policy. Enforce Everywhere.