
Zscaler + PlainID
Enhance Zscaler ZPA with PBAC
Extend your Zero Trust strategy by centralizing and streamlining policy management
Identity Security Challenges in SASE
Effective security requires identity-aware controls integrated into every layer of the enterprise infrastructure. Zero Trust (ZT) best practices require ensuring all enforcement points align with the broader Authorization and ZT strategy to better protect digital assets and maintain a robust security posture.
Benefits of PlainID and the Zscaler Authorizer
Policy Orchestration
PlainID's connection to Zscaler allows for robust policy orchestration by pulling existing native access policies residing in Zscaler and pushing centralized policies for enforcement. This ensures consistent policy enforcement across enterprise technologies and data.
Policy Discovery
Through its rapid integration via the PlainID Authorizer for Zscaler, PlainID discovers policies to give full visibility and help admins identify and understand existing access policies in Zscaler. This facilitates better visibility and management of access control policies.
Token Enrichment
PlainID enriches access tokens with fine-grained entitlements based on verified user approval and policies. This ensures that Zscaler can enforce precise and dynamic access while providing users with the appropriate level of access to critical applications.
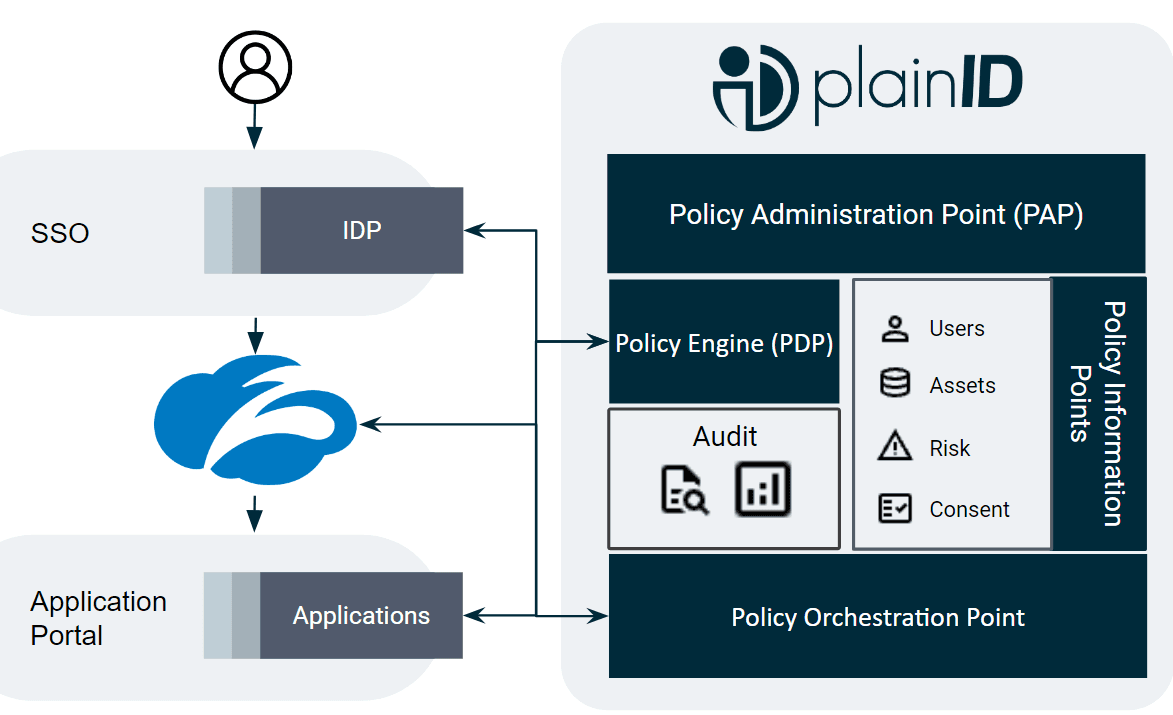
How PlainID works with Zscaler
- PlainID connects to Zscaler for Policy Orchestration, enabling PlainID to pull in and learn about all the access policies currently in Zscaler.
- User request to access a critical application is directed to the Identity Provider (IDP).
- The IDP sends an Authorization request to PlainID to determine user level of access.
- PlainID verifies the user has approval, and the list of fine-grained entitlements they are authorized for, based on the policies.
- The IDP receives the response from PlainID and enriches the access token accordingly.
- The token (i.e. enriched with fine-grained entitlements) is passed to Zscaler.
- Zscaler connects the user to the critical application with read-only access rights.
- Optional: Applications receives Dynamic and Fine-grained access control decisions from PlainID.
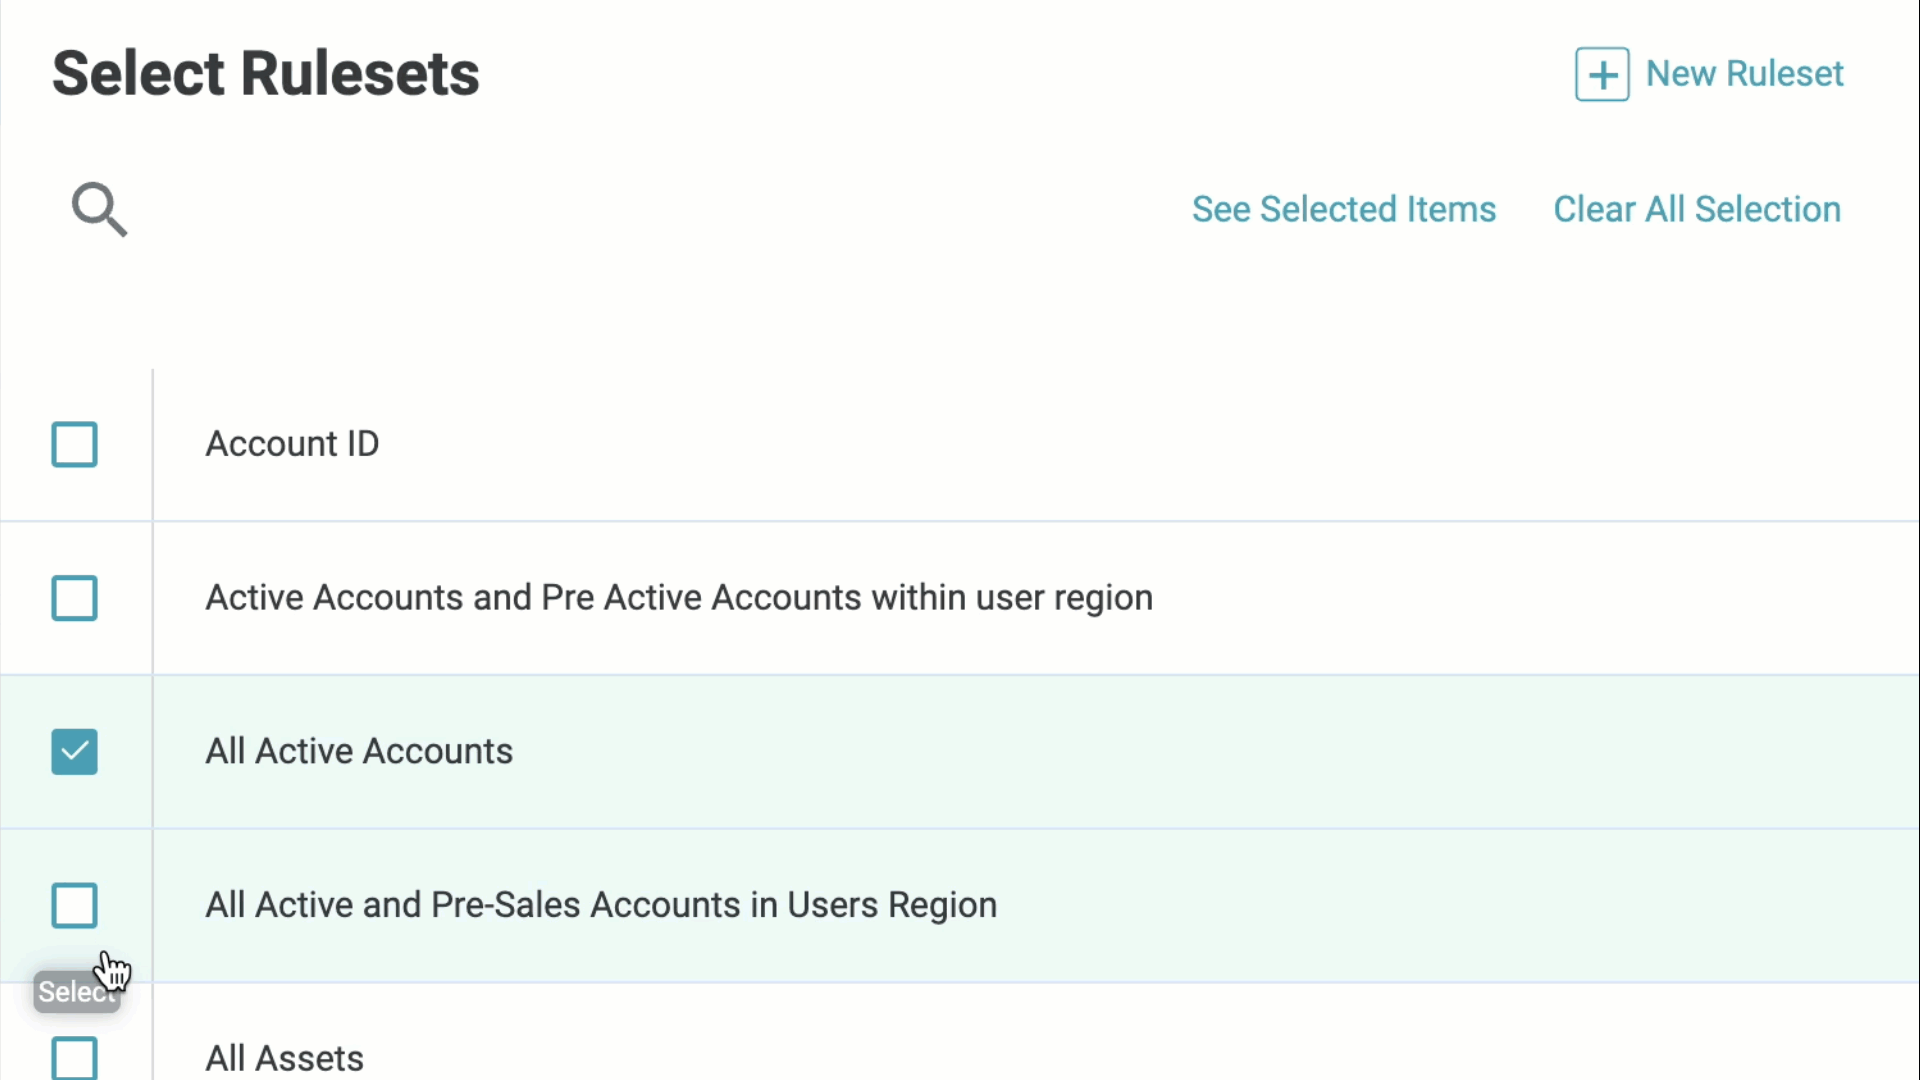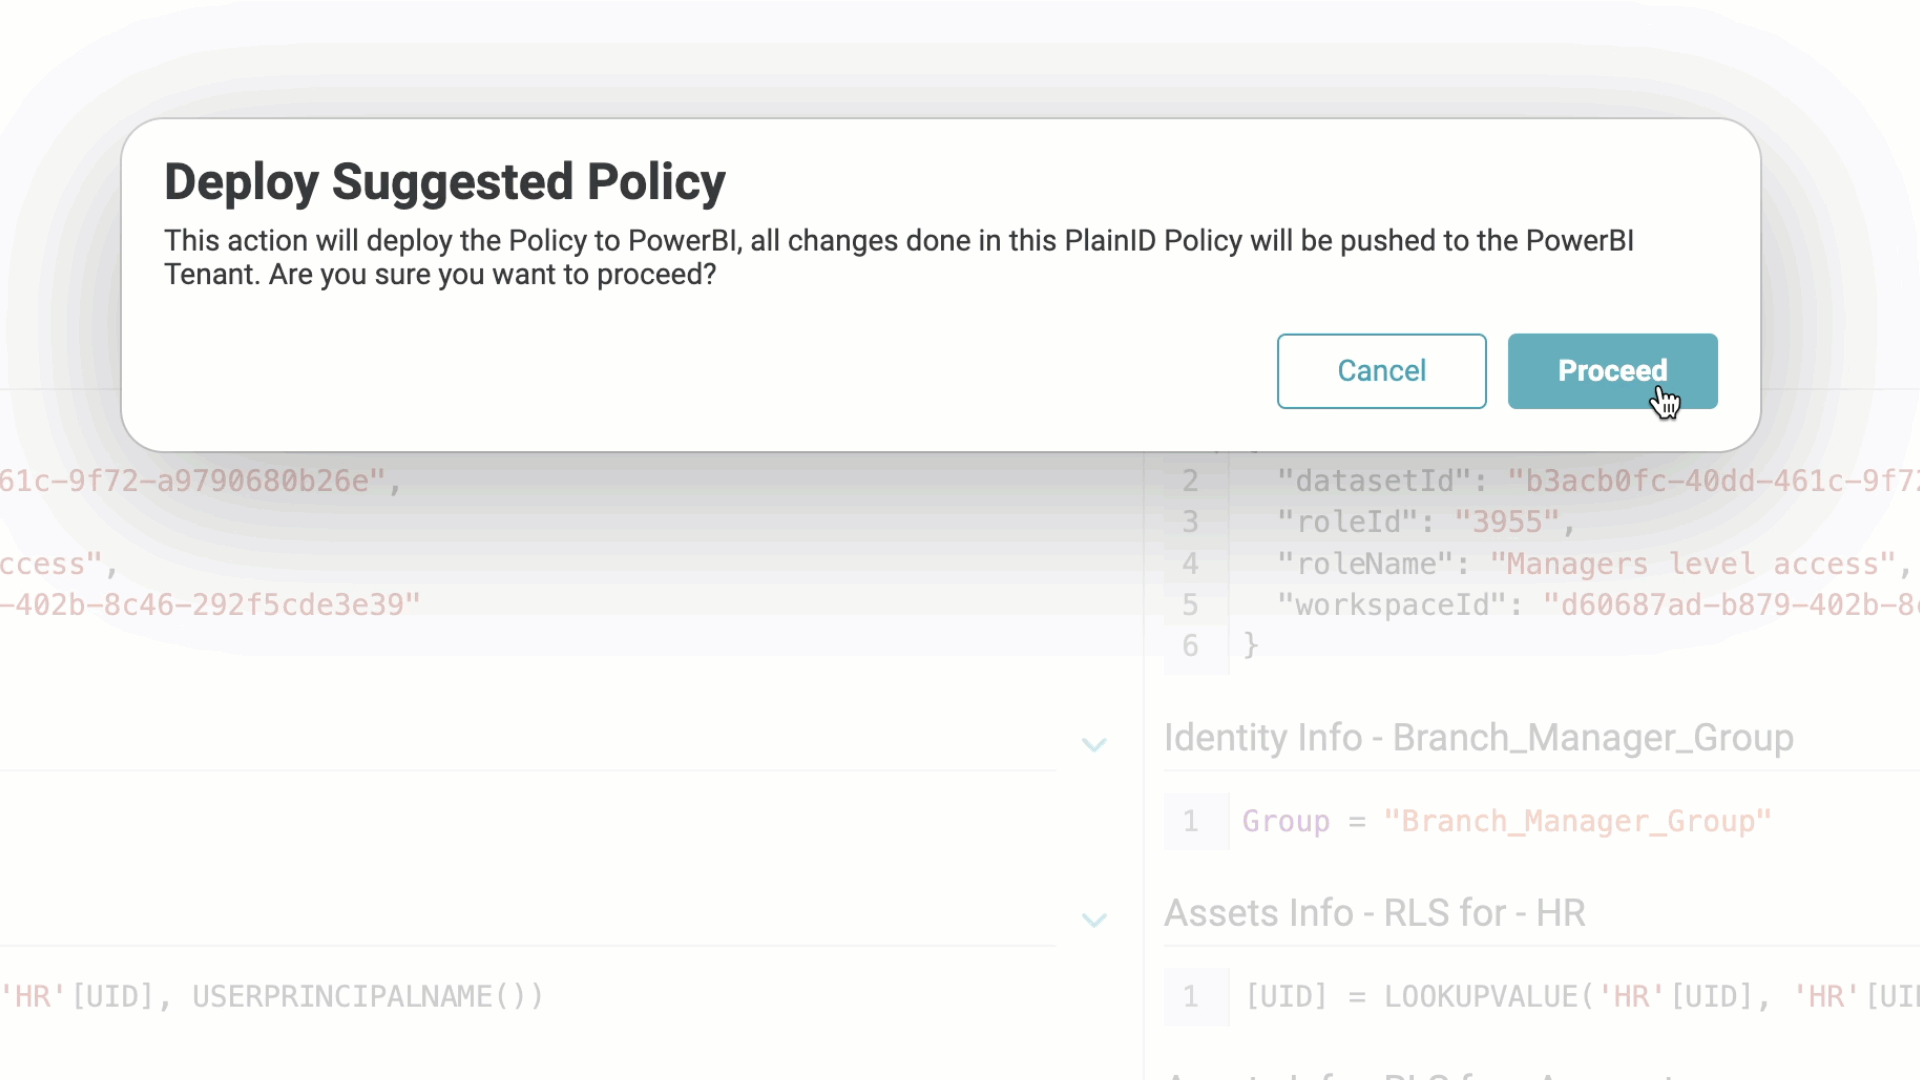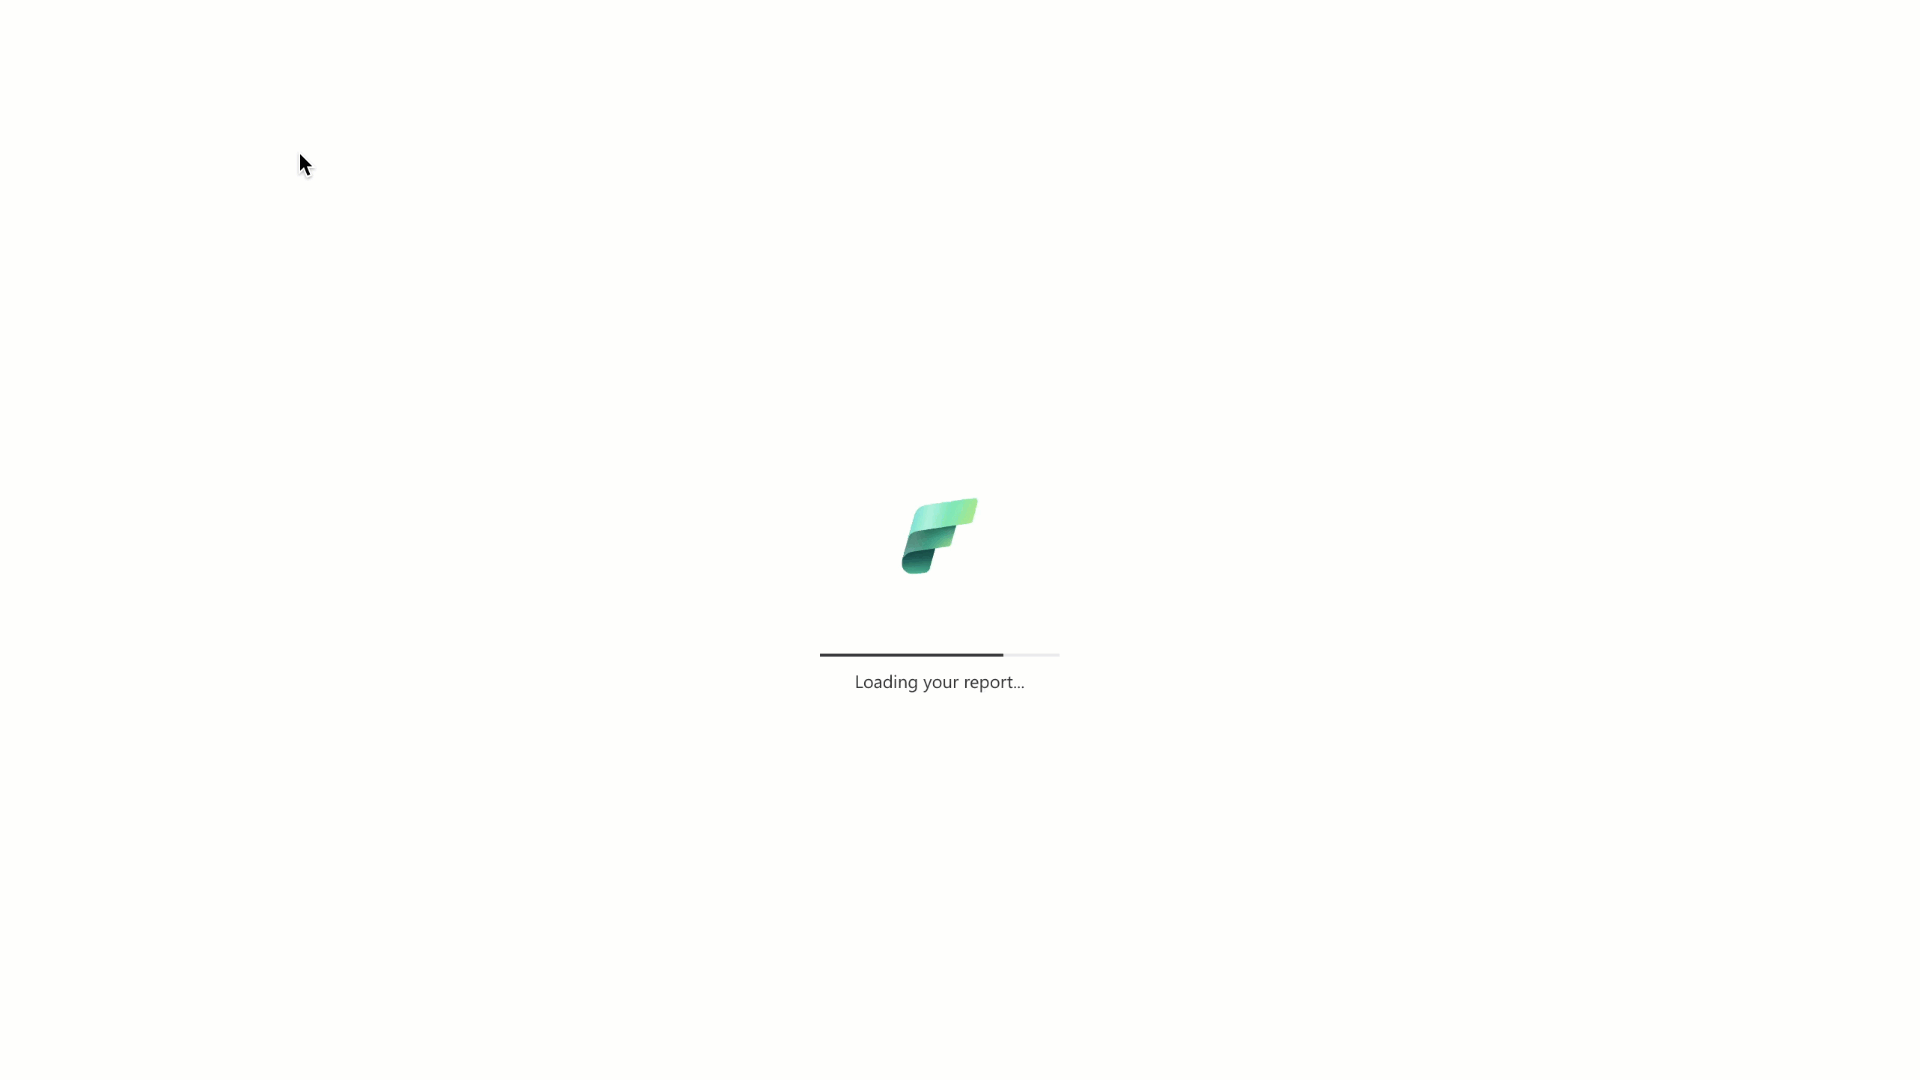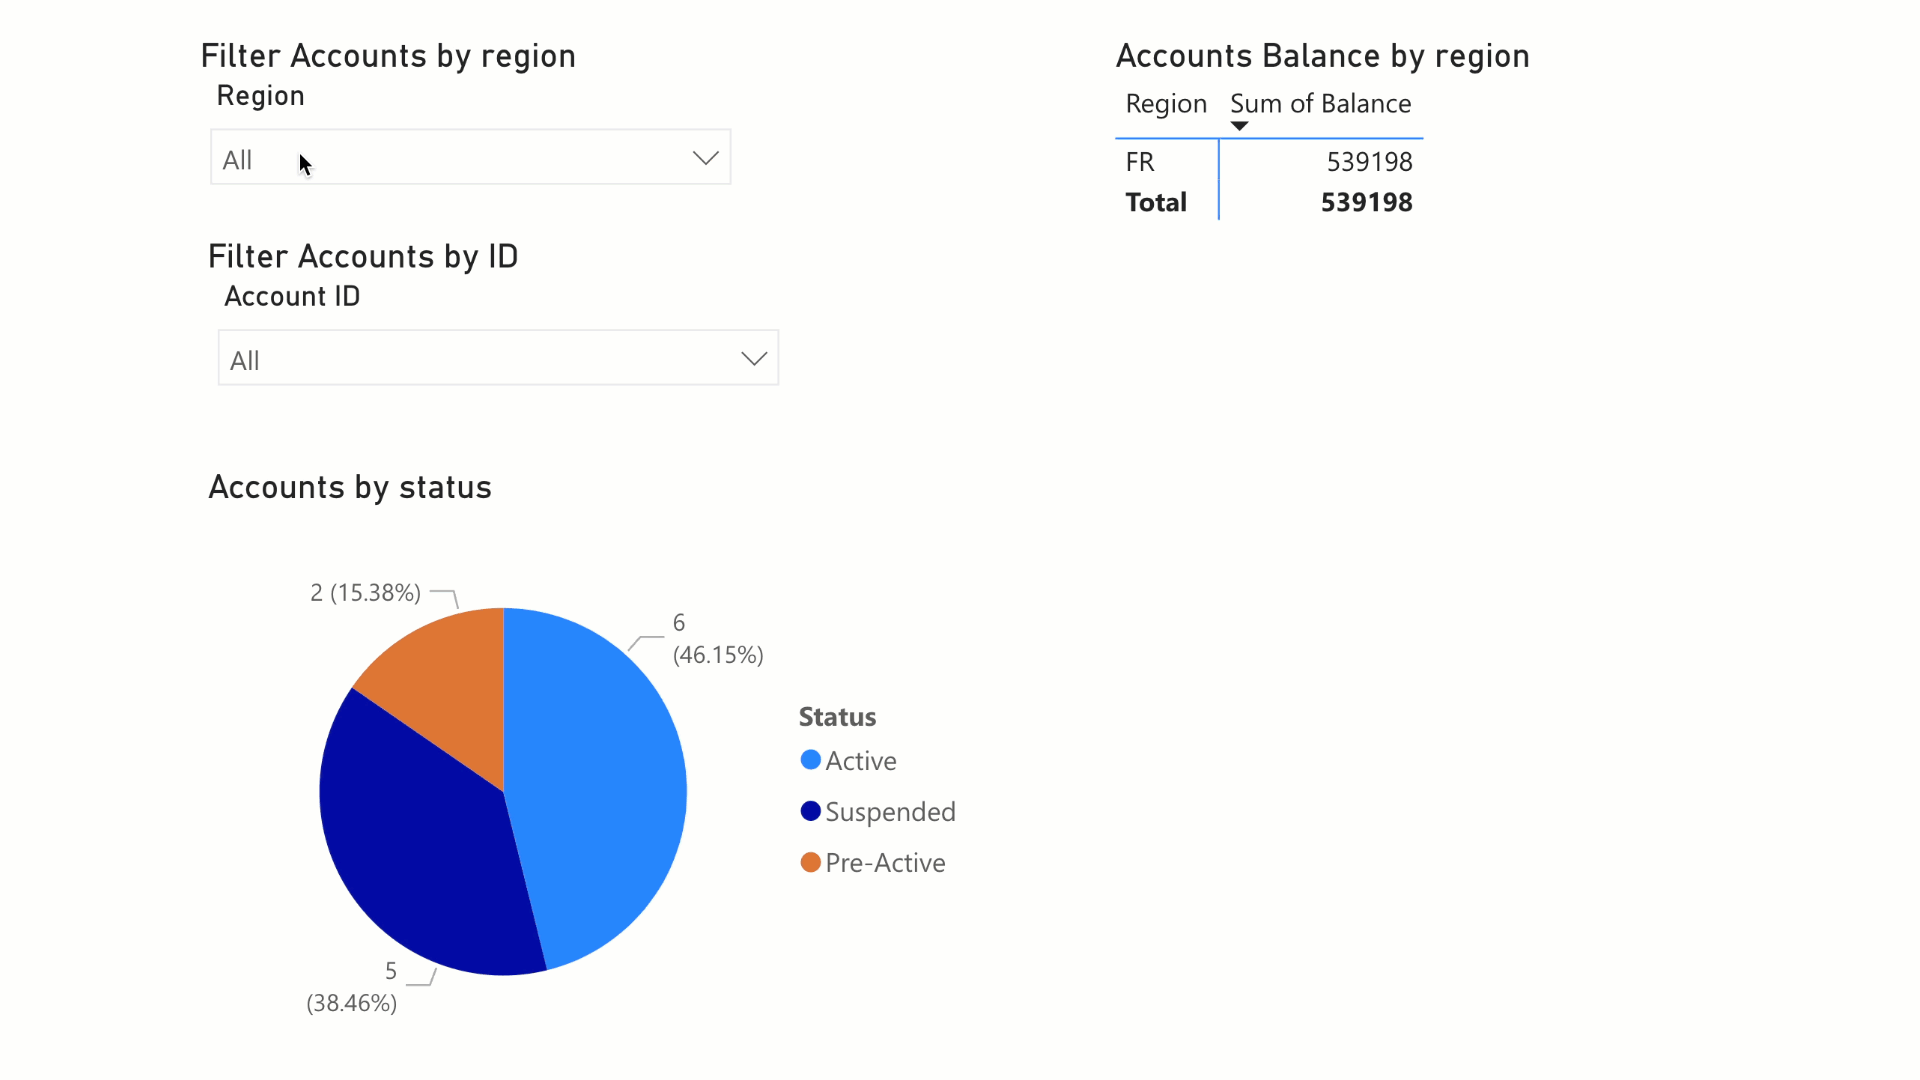
Zscaler and PlainID Demo
The PlainID Platform Benefits
Designed for Identity-centric enterprises, PlainID's Platform is a comprehensive solution that addresses the complexities of modern digital interactions, stopping identity-based threats and unauthorized access to data. The all-in-one platform is the key to unlocking an agile and insightful security posture, defending against identity-based threats in a complex digital world.
PlainID Authorizers
PlainID Authorizers are out-of-the-box integrations that helps enterprises simplify access controls & standardize on PBAC across the technology stack
Enable Secure Data Collaboration
Secure data sharing inside and outside of the organization to maintain data security and privacy.
Minimize Risk with an Identity-first Security Strategy
Connecting identities to digital assets, from applications down to the data layer.
Better Manage Access Policies
Gain end-to-end visibility and control from a centralized management platform.
Explore the Platform
One Platform to Provide you Visibility, Central Policy Management, and Dynamic Authorization.