
Governing AI Agents: The 5-Layer Blueprint for Agentic IAM
Every industrial revolution has forced organizations to master a new control discipline—and the scaling of agentic AI is no exception. As enterprises deploy autonomous software that interprets goals and makes dynamic decisions, legacy static permissions are no longer enough. On the front lines of enterprise security, iC Consult—the leader in implementing complex IAM solutions – is seeing first-hand in the market how fast these unmanaged AI workloads are expanding.
iC Consult, the premier global IT security provider that implements enterprise IAM on the front lines and sees the market shift first-hand, has partnered with PlainID, the leader in Agentic AI Access Management for Fortune 500 enterprises. Together, we are bridging the critical gap between passive “AI safety” content filters and true execution control by uniting identity and security under a single operational model: Agentic IAM.

Why Traditional IAM Fails the AI Agent Test
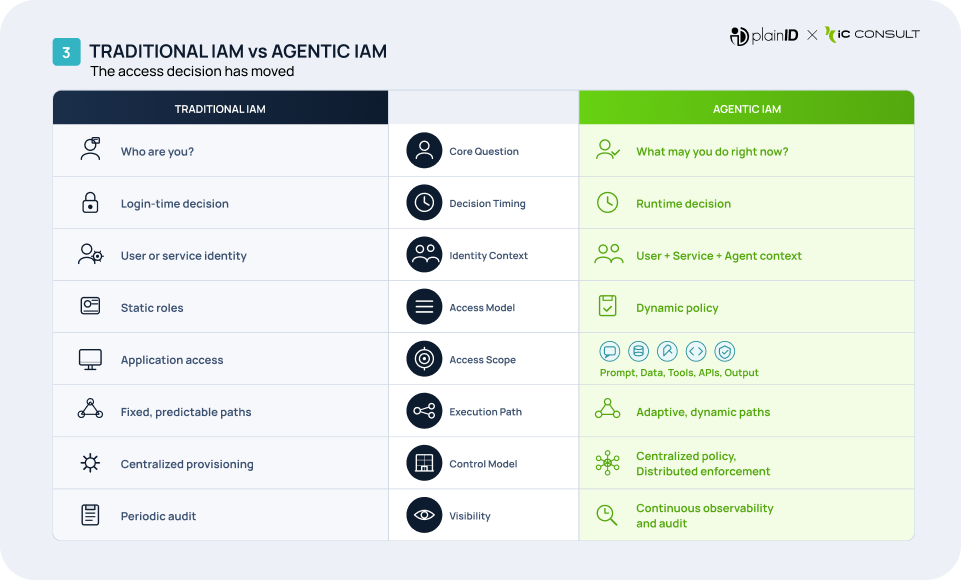
Traditional Identity and Access Management (IAM) was designed for a static world where permissions are pre-assigned and execution paths are predictable. AI agents break these fundamental assumptions in two distinct ways:
- Adaptive Behavior (Not Legacy Scripts): Agents do not execute hardcoded tasks. They interpret prompts and build their own multi-step plan of attack. A static login-time permission cannot foresee what an agent will do three steps down the line.
- The Universal Port (Model Context Protocol): Much like USB-C standardized physical connections, MCP is the universal port for AI. While MCP makes integrations simple, it also creates a massive, unmanaged enterprise attack surface.
Traditional IAM asks: Who are you?
Agentic IAM must ask: What are you allowed to do right now, with what context, using which tools, against which data, and on whose behalf?
The 5-Layer Agentic IAM Architecture
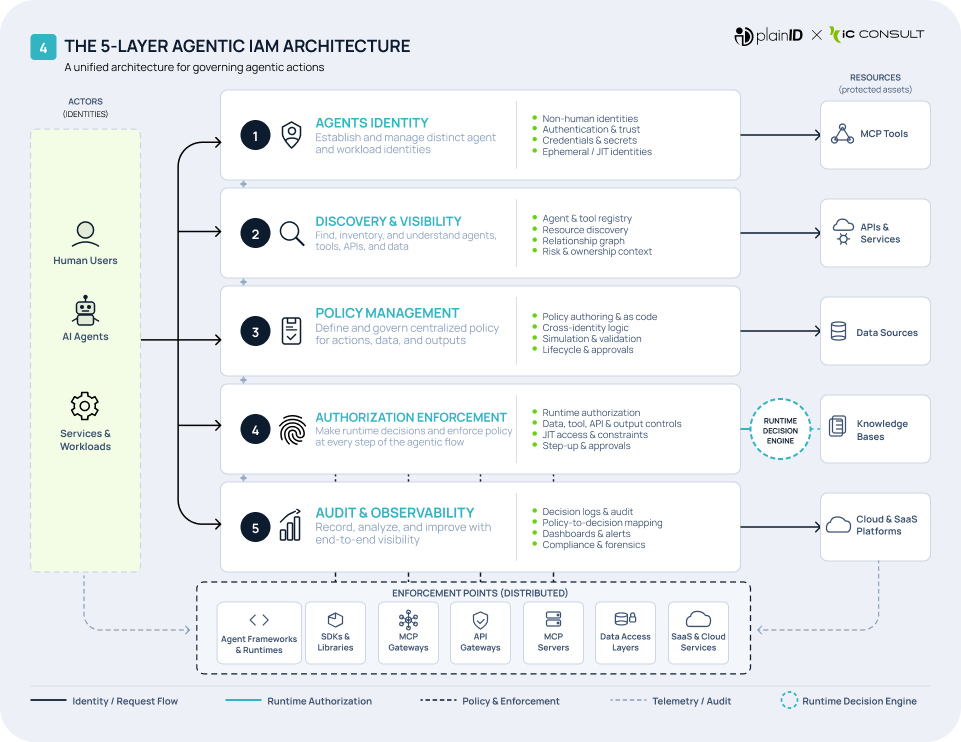
Agentic IAM is the operating model and architectural discipline for governing how human, machine, and AI agent identities authenticate, receive delegated authority, access tools and data, execute actions, and produce outputs under centralized policy and continuous runtime authorization.
Rather than acting as a single product feature, Agentic IAM is built as a coordinated, five-layer control plane designed to provide end-to-end governance:
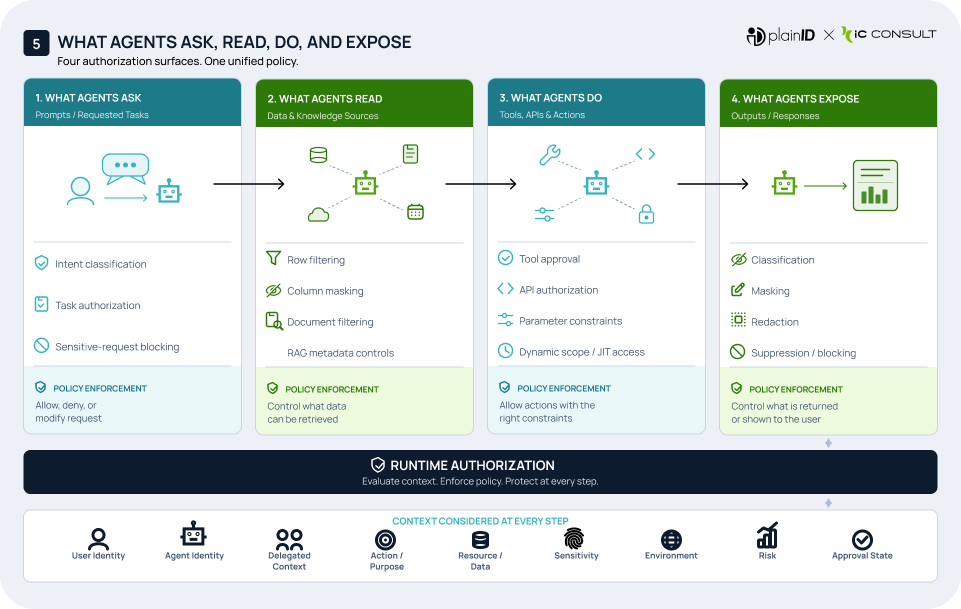
The Four Boundaries of Runtime Authorization
To secure an agent’s dynamic workflow, authorization must be decoupled from the application and enforced continuously across the entire execution path. We look at this through four distinct boundaries:
Bounding Agents with Composite Identity
When an agent executes a transaction, whose permissions should we check? Checking only the agent’s identity leads to unmonitored “agent superpowers”. Checking only the user’s identity ignores whether the agent itself should be performing the action.
The strongest enterprise security pattern is Composite Authorization. In this model, the authorization engine binds the requesting user’s identity and the agent’s identity into a single, unified decision context.
The action is permitted only if the combination of both is authorized, keeping the agent safely bounded by user entitlement while preventing unmonitored privilege escalation.
Step-by-Step Execution: Download the Blueprint
Building an enterprise-grade control plane for AI agents is not a task that can wait. Security teams must act proactively to establish runtime guardrails before ungoverned access paths harden into massive technical debt.
While this post outlines the core concepts, the complete Agentic IAM White Paper (co-authored by iC Consult and PlainID) provides the actionable implementation blueprint.
Inside the full white paper, you will find:
- A comprehensive, 6-step implementation and deployment roadmap.
- The complete Agentic IAM Maturity Assessment framework to evaluate your current identity posture.
- Detailed technical guidelines for integrating dynamic agents with legacy identity systems.
- Production-ready architectural patterns for API Gateway and MCP server enforcement.
Related articles

How to Get Started with Authorization Strategy
Most enterprises already feel the pressure to upgrade their authorization systems to meet the requirements:…
From Security Control to Strategic Enabler: The Business Drivers Behind Modern Authorization
Authorization has traditionally been positioned as a technical control; a necessary component of security architecture,…
AI Agent Authorization: Why Static Roles Break
Give an AI agent a role, and you’ve made a bet you can’t take back…